

Binance Crypto Hack Drains $6.3 Billion, the Largest Theft on Record
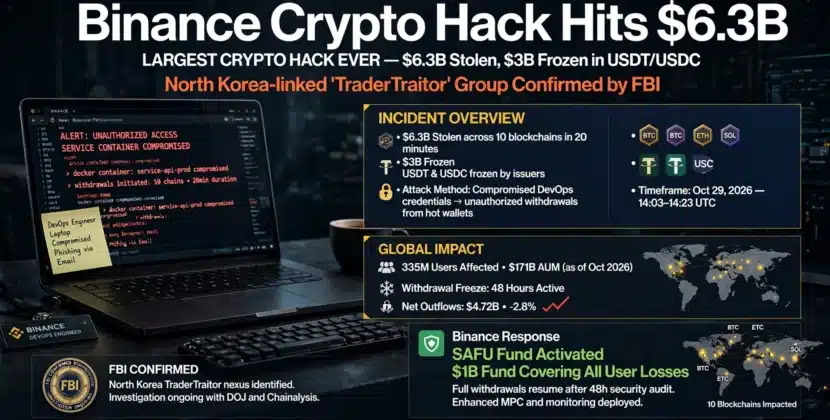
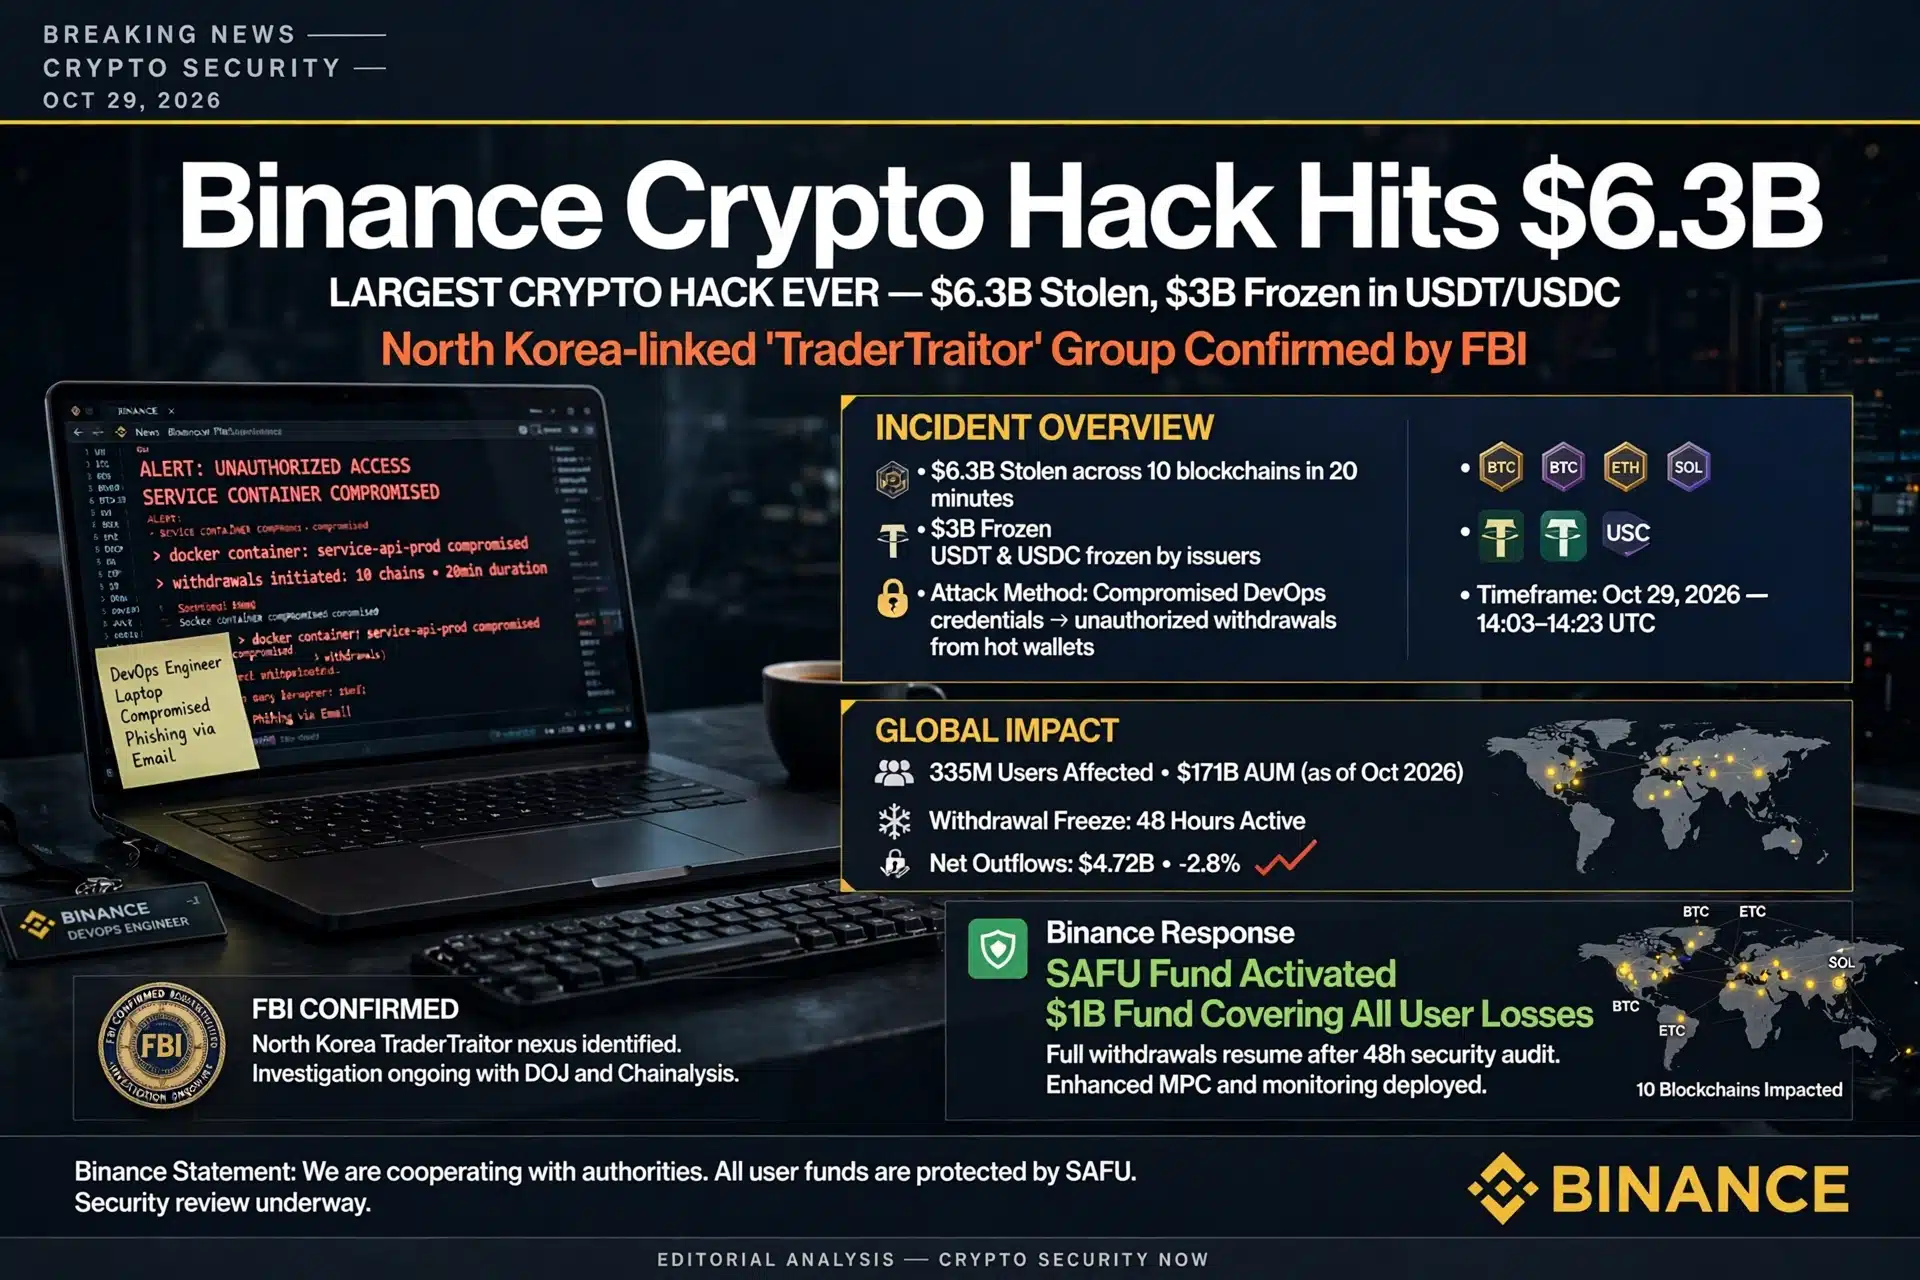
The Binance crypto hack confirmed on October 29, 2026 removed roughly $6.3 billion across ten blockchains in about 20 minutes, making it the largest cryptocurrency theft ever recorded, and the Binance crypto hack now has the FBI, the US Secret Service and blockchain intelligence firms tracing funds ahead of a phased withdrawal restart. Binance says no wallet private keys leaked and that it will cover every loss through its SAFU fund, and by early October 30 roughly $2.7 billion was already frozen. US holders of Binance.US assets were not directly hit, but the event still reshapes how US regulators, banks and exchanges think about custody risk.
Key Takeaways:
- – Binance suspended withdrawals across multiple networks on October 29, 2026 after on-chain analysts flagged massive outflows; founder Changpeng Zhao called it a hack while it was underway.
- – Total losses are about $6.3 billion per TRM Labs, dwarfing the February 2025 Bybit theft of $1.5 billion that previously held the record.
- – Binance’s preliminary finding: a compromised DevOps engineer’s laptop gave attackers access to a service container that could submit unauthorized withdrawal transactions.
- – Tether froze about $1.56 billion in USDT and Circle froze roughly $800 million in USDC; TRM counted about $2.7 billion frozen by 00:30 UTC October 30.
- – TRM Labs attributes the attack with high confidence to TraderTraitor, a North Korean Lazarus-linked group; Binance set aside $5 billion and bought another $1.34 billion in tokens to cover users.
What happened on October 29
The collapse unfolded in public. Wallet-draining reports escalated through the day until Binance paused withdrawals on multiple networks and stated that user funds were completely safe, a stability message it repeated as the outflow total grew. Zhao’s blunt acknowledgment that it looked like a hack on Binance came before the exchange had ruled one out, reflecting how visible the on-chain drains already were. Within the first movement window, the attacker moved the entire haul across ten blockchains in roughly 20 minutes, a speed made possible by the exchange’s own hot-wallet signing infrastructure, which had accepted the theft transactions as valid.
The technical heart of the case, per TRM Labs’ on-chain review, is subtle. On Ethereum the attackers used a batch of 50 pre-signed delegations from a Binance hot wallet, submitted under the EIP-7702 delegation mechanism, with one matching the target at execution time, plus validly signed transactions on the nine other chains. The implication researchers draw is that the attacker could induce Binance’s hot-wallet signing system to sign arbitrary transactions, an infrastructure compromise far deeper than a leaked key.
How the attackers got in
Binance’s own preliminary finding points at an entry point most US companies will recognize: a compromised DevOps engineer’s laptop. From that machine the intruder reached a service container and submitted unauthorized withdrawal transactions. This is the same opening move that flattened major US retailers and hospitals over the past five years, and it converts the hack from a crypto puzzle into a classic enterprise security incident with a cryptographic tail. Binance’s extraction playbook mirrors that too, freezing detected chains where issuers control tools, compensating directly, and publishing a proof of reserves to rebuild trust.
The “no private keys leaked” claim matters for victims, and Binance has repeated it along with its full-coverage commitment. The exchange says it set aside $5 billion and bought an additional $1.34 billion in tokens to make depositors whole through the SAFU emergency facility, and it planned to restore withdrawals in phases within roughly 34 hours, according to its October 30 update and subsequent reporting.
Who did it and what froze
Attribution is unusually convergent. TRM Labs assigns the operation to TraderTraitor, the North Korean Lazarus-umbrella grouping responsible for some of history’s largest exchange thefts, with high confidence, citing on-chain and off-chain indicators that mirror its prior work on Bybit and the KelpDAO case from April 2026. Chainalysis’s chief executive Jonathan Levin concurred publicly, and per reporting other independent trackers reached the same conclusion. Binance has not officially named a culprit, and no agency has formally done so either.
Freezing raced the laundering money. Tether froze about $1.56 billion of USDT, Circle froze roughly $800 million of USDC, and Arbitrum’s security council siphoned some $30 million out of an attacker-controlled wallet on its chain before the attackers could consolidate it. TRM’s tally put about $2.7 billion immobilized by early October 30 UTC. The unfrozen remainder is the hard problem: researchers estimate the thieves still hold over 420,000 ETH and 18,270 BTC, worth about $2.4 billion, which no issuer can freeze, and they sold the seized stablecoins at discounts of more than 10 percent as they converted into those harder assets.
What it means for US holders and regulation
The direct US financial exposure is limited because Binance.US, the domestic-facing platform, operates separately, but the knock-on effects reach US wallets three ways. First, the frozen reserve machinery that absorbed the loss is paid for by the exchange’s balance sheet, which raises systemic questions about whether exchange theft at scale is insurable at all. Second, the FBI and Secret Service are working with Binance on tracing, which widens law enforcement pressure on the North Korean cyber program Washington has long cited as a sanctions-evasion engine. Third, the public word on attribution arrived on October 30 when the President, asked about the hack in the Oval Office, said the US was looking into North Korea’s involvement but that the country did not know yet who was responsible, while noting Binance said it planned to make users whole.
The event also compresses the security debate for everyday US crypto users. Self-custody removes exchange-platform risk but concentrates personal key risk, which remains the larger killer of small-investor funds; the Bybit lesson applies identically here, that hardware-secured self-custody of meaningful holdings and minimal exchange balances are the conservative posture.
What happens next
Watch the phased withdrawal restart, promised within about 34 hours of the pause, and the updated proof of reserves Binance said it would publish; both are direct evidence for the “funds are safe” claim. The laundering chase will run for months through mixers, bridges and OTC desks, and the recoverable share of the unfrozen $2.4 billion depends on cooperation from market makers and law-enforcement pressure on intermediaries. A confirmed attribution to North Korean operators will feed the ongoing case for harder network-level defenses against a state that now has benchmark-setting heists in 2025 and 2026. For Congress, the immediate deliverable is custody and financial-incident reporting standards that make a DevOps-laptop compromise less likely to become a $6.3 billion customer loss at any capital markets venue users rely on.
Frequently Asked Questions
How much did the Binance hack steal?
About $6.3 billion per TRM Labs, extracted from Binance wallets across ten blockchains in roughly 20 minutes on October 29, 2026, exceeding the February 2025 Bybit theft of $1.5 billion that had been the largest on record.
Is it safe to leave funds on Binance?
Binance states user funds are safe, says no wallet private keys leaked, and says SAFU plus corporate funds will cover all losses, with withdrawals resuming in phases. The event nonetheless demonstrates that exchange operational security is a single point of failure, so the conservative posture most security researchers repeat is to hold long-term assets in self-custody and keep only working balances on exchanges.
Who hacked Binance in October 2026?
Blockchain intelligence firm TRM Labs attributes the theft with high confidence to TraderTraitor, a North Korean Lazarus-linked group, citing on-chain and off-chain indicators matching its prior operations; Chainalysis’s chief executive and other trackers independently concur. Binance has not officially assigned blame, and no government has formally named a culprit.
Sources:
- https://www.securityweek.com/6-billion-binance-hack-bears-hallmarks-of-north-koreas-tradertraitor/
- https://techcrunch.com/2026/10/29/binance-pauses-withdrawals-as-hackers-suspected-of-stealing-billions-in-crypto/
- https://www.forbesafrica.com/current-affairs/2026/10/31/binance-says-it-plans-to-resume-withdrawals-this-weekend-after-6-3-billion-hack