Armonk, New York.  

Most enterprise technology announcements get a lot of attention, but often don’t lead to real change. This time, it’s different. On June 4, 2026, IBM and Google Cloud announced a new Google Cloud practice, Google IBM Consulting. This move puts thousands of specialized digital workers into the central operations of major global companies. These are not just chatbots for HR questions. They are genuine AI agents designed to handle complex, multi-step business tasks across banking, government, insurance, and hospital systems.  

The scale of this effort stands out. The new Google Cloud practice adds thousands of Google Cloud-certified IBM consultants and engineers to help companies use AI, modernize legacy systems, and manage technology across complex environments. This is a multi-billion-dollar opportunity for both IBM and Google. That number is real, showing how committed both companies are to making enterprise scaling the next big business move.  

What the IBM and Google Cloud Strategic Partnership Scaling Gemini Enterprise Agentic Models Actually Means 

If you look past the press release language, the plan is clear. IBM has spent decades working inside large organizations. Its consultants know the old mainframes that handle insurance payouts, the government databases that need several manual steps to process requests, and the retail systems that still run nightly batch jobs. Google, on the other hand, has built a powerful AI platform with its Gemini Enterprise agent platform, but it hasn’t had IBM’s deep connections within enterprises.   

The new practice brings together IBM’s industry expertise and its AI-powered delivery platform. IBM consulting advantage with Google Cloud’s Gemini Enterprise agent platform, cybersecurity tools, and data infrastructure. Simply put, IBM understands where the inefficiencies lie, and now Google has the technology to fix them at scale.  

The Agents Themselves: Sector by Sector 

This is where the announcement moves from abstract to concrete. IBM is creating a portfolio of industry-specific agents built on IBM Consulting Advantage and optimized for Gemini Enterprise. These agents will be used in banking, government, retail, telecommunications, energy, security, insurance, and life sciences. They will help organizations automate tasks, make better decisions, and speed up operations using Gemini models.  

For example, in a regional bank, a loan modification request might currently pass through five departments over two weeks. Analysts pull credit data behind the scenes, compliance officers check regulations, and relationship managers send follow-up emails. An industry-specific agent in this process would not replace the compliance officer’s judgment, but it would manage the rest. It would gather credit data, highlight regulatory items for review, draft client messages, and record every action. The human still makes the final decision while the agent handles routine tasks.  

This approach works in other sectors, too. In life sciences, agents can organize clinical trial data among different research sites. In telecommunications, they can automate network fault checks that now need overnight tickets and morning calls.  

IBM Consulting Advantage as the Delivery Engine 

IBM Consulting Advantage is the foundation that allows this to happen as quickly as IBM promises. IBM’s pre-built tools, reusable agents, and proven methods can be used with Google Cloud’s agent platform, governance controls, and safety features. This helps organizations go from planning to deployment faster and more consistently.   

This matters for enterprise scaling because traditional consulting is slow. Usually, a firm studies a client’s setup for months, creates a custom solution, tests it in one department, and then rolls it out over a year or more. IBM Consulting Advantage speeds this up by offering reusable agent templates that consultants can adopt for each client rather than starting from scratch. For example, a telecommunications agent built for one company can be used as a base for the next. This way, knowledge builds over time rather than being lost after each project.  

The Governance Question Nobody Is Asking Loudly Enough 

IBM Consulting will help create standard interface patterns and solutions to connect enterprise data to Gemini. They will use an open, flexible approach with interfaces tailored to each client’s system. This will help organizations bring their data together and scale Gemini-based AI more easily.  

This pliability is both an advantage and a risk. When thousands of Gemini AI agents operate simultaneously within a hospital network or government agency, it is important to know who is monitoring them. Google Cloud’s governance controls are built into the Gemini Enterprise platform, but using them effectively across different types of enterprise systems, some cloud-based, some hybrid, some still using old on-premises infrastructure, requires the kind of human expertise that IBM provides.  

At its core, the IBM and Google strategic partnership to scale Gemini Enterprise agent technologies is a bet that human institutional knowledge and AI execution capability are more powerful together than either alone. The agents do not replace IBM’s consultants. Instead, they help those consultants deliver more value in each project.  

What American Professionals Should Watch 

For executives at mid-sized and large companies, this partnership means practical AI adoption is happening faster. The question is no longer if you should use AI agents, but whether your company will be ahead or behind others in your industry. The Google Cloud practice is a multi-billion-dollar services opportunity, with IBM and Google each delivering unique strengths to help clients adopt AI and modernize their systems.  

For knowledge workers, the main issue is how workflows will change. The administrative parts of most corporate jobs, including gathering data, updating statuses, and handling documentation, are exactly what Gemini AI agents are designed to take over. This does not always mean job cuts. More likely, professionals who know how to manage and improve these agents will be in higher demand than those who do not.  

The companies that learn how to manage these systems well, not just set them up, will define the future of enterprise AI for the next decade. IBM and Google have just created the first real guide.

Source: How Capcom Is Leading the Way for Enterprise Agentic AI 
Seattle, Washington 

Most Americans don’t just wait for any sale to start; they wait for one that’s truly worth it. Amazon has just given everyone a reason to pay attention. Prime Day 2026 is set for June 23 to June 26, making it the earliest iteration of the event since 2021 and the second year in a row with a four-day summer sale. Even better, the best deals are already available. 

Early Amazon Prime Day Access Is the New Competitive Edge 

There was a time when smart shoppers marked their planners and stayed up until midnight to catch the first Prime Day deals. That has changed. Now, Amazon is giving early shoppers real discounts instead of just temporary promotions. 

Prime members can now save up to 60% on Alexa+ devices like the Echo Dot Max, Echo Show 11, and the Echo Show 8+ Carrera Smart Glasses bundle. There are also discounts of up to 65% on Kindle, Ring, Echo, Fire TV, Blink, and eero products. These are real deals, not just previews. If you want the Kindle Colorsoft Essentials bundle or the Ring Battery Doorbell Plus, you don’t have to wait three weeks to get a big discount. 

This is important because the four-day summer sale, which Amazon started testing in 2025, now seems here to stay. With more time, both shoppers and retailers have more chances to stack discounts, compare prices, and plan purchases. These are the habits that set careful shoppers apart from those who buy on impulse. 

Electronics Markdowns Already in Motion 

The big electronics markdowns that dominate Prime Day conversations are not arriving uniformly. Certain categories are moving now. Shoppers can already access up to 80% off Kindle books, up to 65% off print books in any genre, and three free months of Kindle Unlimited and Audible if you qualify. 

If your household has been putting off a smart home upgrade, now is a good time to act. The Echo Show 11 is 60% off and can be the main device for controlling lights, thermostats, security cameras, and music in one place. Waiting until the official sale on June 23 at 12:01 a.m. PDT could be risky. Popular options might sell out, and prices may not stay this low. 

Take, for example, a family in suburban Columbus, Ohio, with two incomes, two kids, and a list of technology improvements they’ve put off since last Black Friday. With a 65% discount on eero routers and a markdown on the Ring Doorbell Plus, they can upgrade their home security for about half the usual price. This isn’t merely a promise. it’s a real savings you can get right now. 

Alexa Shopping Alerts Remodel the Research Phase 

One of the biggest changes for Prime Day 2026 is how Amazon uses Alexa Shopping Alerts to make shopping easier. Members can ask Alexa for a personalized deals guide based on their shopping history and preferences. Just tap the “+” icon in the Alexa for Shopping chat bar and choose Prime Day deals. 

This is a big change from the early days of Prime Day, when shoppers had to sort through thousands of deals with no personal guidance. Now, if you bought a Blink camera two years ago and a Fire TV Stick last spring, you’ll get alerts for deals that make sense for you, not just random promotions. 

Amazon is also holding a sweepstakes for Prime members who set up a deal alert with Alexa. You could win a $1,000 Amazon gift card, and 100 winners will be chosen by Prime Day. This encourages people to use the tool and get involved before the sale starts, which leads to more shoppers making purchases when the event begins. 

A Budget Buying Guide Built Around the Calendar 

With Prime Day 2026 taking place in June rather than July, American households may want to rethink their summer spending plans. Since Prime Day comes before July Fourth, the FIFA World Cup, and Father’s Day, expect deals themed around these events. For example, a family planning a Fourth of July party could use discounts on smart speakers and Fire TV Sticks to set up their backyard entertainment before the holiday. 

A good budget plan for Prime Day should consider three things: what you need right now, what you’ll need before summer ends, and what you might buy if the discount is big enough. 

Grocery spending counts too. Right now, Prime members who spend $15 or more on a qualifying online grocery order can enter to win free groceries for a year in Amazon’s $1 million sweepstakes. Each week, 100 winners are announced leading up to Prime Day. For families already shopping at Amazon Fresh or Whole Foods Market, this is a big incentive. 

The Amazon Prime Day Early Savings Registration and Electronics Discount Tracking Guide Strategy 

Treating Amazon Prime Day early savings registration and electronics discount tracking as a passive exercise is the most common mistake first-time Prime Day shoppers make. The competitive advantage belongs to members who actively engage the system  and in 2026, that system is more responsive than ever. 

The steps are simple. First, check that you have a Prime membership. It’s $14.99 per month or $139 per year, which saves about $40 over twelve months. Students and Prime for Young Adults can pay as little as $7.49 per month after a free six-month trial. Next, turn on Alexa Shopping Alerts for the products you want, which also enters you into the $1,000 gift card sweepstakes. Finally, compare the current early deals to your shopping list .the 60% off Alexa+ devices are available now, not just on June 23. 

Prime members with an Amazon Prime Visa card can get 10% cash back on eligible deals in beauty, clothing, PCs, electronics, and personal care during the sale. Combining discounts with cashback can add up to big savings, especially on purchases over $100. 

The Chain Reaction on Retail 

Prime Day doesn’t happen in isolation. Each year, when it’s announced, competitors like Target, Walmart, and Best Buy launch their own sales at the same time to keep shoppers from spending only on Amazon. This competition is good for shoppers, especially those willing to compare deals among different stores. 

Prime Day 2026 spans more than 35 product categories across 26 countries, underscoring just how expansive Amazon’s reach is this year. When a company this large runs a four-day event with early discounts, competitors respond. The resulting mid-summer price war usually brings the biggest discounts in electronics, appliances, and subscription services the areas where most American families spend the most. 

The strategic window is now. The deals are live. The early Amazon Prime Day opportunity does not require a countdown timer. it requires a shopping list and a Prime membership. By June 23, the savviest shoppers will already have most of their carts filled.

Source: When is Amazon Prime Day 2026? Shop deals June 23-26 

Santa Clara, California 

Every hour, a large hospital system in the United States processes between 5,000 and 10,000 patient specimens. Blood draws, biopsies, and culture samples are each tagged, sorted, and routed through a clinical laboratory. If a label is missed or a barcode is misread, a diagnosis can be delayed by 24 hours or more. For patients waiting on cancer staging results or sepsis confirmation, that delay is not simply a minor inconvenience. It is a real and painful wait. Intel Hardware Accelerates this process by using a new generation of embedded silicon placed directly inside Medical Lab Robots, quietly changing what clinical automation can do in the lab. 

Why the Old Architecture Couldn’t Keep Up 

For years, clinical lab robots used a split system: cameras were on the machine, but the computing was done in a server room connected by a network. The robot would take a picture of a specimen vial, compress the image, transmit it over the network to a processing server, wait for the result, and then act. While this looked good in theory, in reality, delays added up. Network traffic congestion, server overload during shift changes, and the distance between the sensor and processor caused slowdowns right when speed was most important. 

In a busy lab with six robotic arms working at once, processing queues could go over 200 milliseconds per specimen during peak times. When you multiply that delay by 8,000 vials in an eight-hour shift, the numbers add up fast. 

Core Ultra Edge Silicon changes things by bringing the sensor and judgment together, removing any delay between them. 

What Intel’s Embedded Core Ultra Actually Does Inside a Lab Robot 

Intel’s newest Core Ultra series, especially the processors designed for embedded industrial and medical applications, combines a CPU, a dedicated GPU tile, and a neural processing unit (NPU) in a single package. The NPU is especially important in clinical settings. It handles Real-Time Image Processing of multispectral camera feeds without sending any data to an external server. 

Think about what a modern specimen-sorting robot needs to see. Reading a barcode is easy. The real challenge is inspecting the sample itself: spotting hemolysis (a pinkish color indicating red blood cells have ruptured), lipemia (a cloudy appearance from excess fat in the blood), or icterus (a yellow color from high bilirubin). These visual quality checks once needed a trained lab technician. Now, they are spectral classification problems that an NPU with a good neural network can solve in less than three milliseconds per sample. 

At three milliseconds per classification, one robotic arm could process up to 20,000 specimens per hour using vision processing alone. This is much higher than what network-dependent systems could handle. 

The Intel Core Ultra embedded processor clinical laboratory robotics deployment specifications published by Intel’s industrial solutions group indicate sustained NPU performance of up to 13 TOPS (tera-operations per second) within a thermal design envelope compatible with fanless, sealed laboratory enclosures. That matters because clinical environments demand equipment that can be wiped down with disinfectants; fan vents are ingress points for contamination. 

Clinical Automation Gets a Local Intelligence Layer 

Moving to Local Machine Vision is more than merely a performance boost. It changes the intelligence embedded in the clinical workflow. 

With the cloud-dependent model, specimen images were transferred across hospital networks and sometimes to external processing systems. HIPAA compliance teams had to spend a lot of time reviewing data flows, configuring encryption, and logging every transmission. If a packet was sent to the wrong place, it wasn’t only an IT problem. It could mean a patient data breach. 

With Clinical Automation powered by Core Ultra Edge Silicon, the image is processed right on the machine that captured it. The specimen photo stays on the robotic arm’s processor. Only a structured data record leaves the robot, including the specimen ID, quality score, and routing instructions. No raw image data goes over the network. This makes compliance much simpler and greatly reduces the risk of a data breach from imaging. 

Mayo Clinic’s laboratory informatics team outlined this exact architecture preference in a 2024 white paper on edge deployment for diagnostic automation, noting that local inference “eliminates an entire class of regulatory exposure” while simultaneously reducing the infrastructure cost of running high-bandwidth imaging networks across sprawling hospital campuses. 

The Speed Dividend Reaches Patients 

When a lab can verify, sort, and route 4,000 specimens per hour instead of 1,800, as shown in third-party benchmarks comparing network-dependent and edge-native systems, the benefits reach families waiting for results. 

Routine chemistry panels that used to take six hours during busy times now finish in under three hours at places using edge-native robotics. For emergency doctors making quick decisions about sepsis or heart issues, cutting lab turnaround time by three hours is a big deal. It can mean starting targeted antibiotics in the second hour instead of the fifth. 

Intel Hardware Accelerates this conclusion not by replacing clinical expertise, but by removing the delays that old hardware caused in automated systems. The robot does not become better at medicine itself. Instead, it gets faster at tasks like sorting, routing, and verifying, so that human experts can focus on what only they can do. 

What Comes Next for Medical Lab Robots 

The Intel Core Ultra embedded processor clinical laboratory robotics deployment specifications roadmap points toward heterogeneous compute scaling: future generations will likely have higher-TOPS NPU tiles and greater memory bandwidth to support multiple types of analysis simultaneously, such as visual inspection, RFID checks, and predictive maintenance signals, all within a single onboard decision process. 

Real-Time Image Processing will go beyond checking specimen quality and move into predictive analytics. For example, an onboard model could spot a pattern in 200 samples from one collection team that suggests a pre-analytical error, such as centrifuging at the wrong time, before the samples reach the analyzer. The robot will become less of a sorter and more of an active quality monitor. 

For healthcare executives planning equipment purchases in the next two to three years, the question is no longer whether to use Clinical Automation with Local Machine Vision. Now, the focus is on which medical workflows to automate first and how to set up informatics systems to handle the large volume of structured data that edge-native robotics will generate. The hardware challenge has already been solved.

Source: Intel Newsroom 

San Jose, California  

A network flaw that gives attackers the digital analog of a building’s master keycard, opening every server room, data closet, and administrative terminal, is not simply a theory. This is the reality network administrators across the United States faced this week when Cisco issued an urgent advisory confirming active exploitation of CVE-2026-20245, a Cisco Software Zero-Day found in its widely used Catalyst SD-WAN networking platform. The vulnerability is being blocked now by enterprise security teams, as attackers are already trying to exploit it. 

The Anatomy of a Catalyst SD-WAN Flaw 

SD-WAN, or Software-Defined Wide Area Networking, is a core part of modern enterprise infrastructure. Hospitals use it to send patient records. Regional banks rely on it for transaction data. Major logistics hubs use it to keep shipment information up to date. When Cisco’s SD-WAN has a vulnerability, it is not simply an IT issue it threatens the daily operations of institutions that people depend on. 

CVE-2026-20245 is found in the web-based management interface of Cisco Catalyst SD-WAN Manager. This flaw is a command injection vulnerability, meaning an unauthenticated remote attacker can send a malicious HTTP request that the system interprets as a valid operating system command. When this happens, the attacker gets root privilege, the highest level of access on a Linux-based system. From there, they can read configuration files, steal encryption keys, install backdoors, or stop the device from working. No password or internal network access is needed just a carefully crafted packet sent over the public internet. 

Cisco’s Product Security Incident Response Team (PSIRT) confirmed that the vulnerability has a CVSS score of 9.8 out of 10, which puts it in the “Critical” category. The agency has not said which threat actor or group is exploiting it, but the advisory’s statement, “Cisco is aware of active exploitation in the wild,” makes it clear that waiting for a scheduled patch is not an option. 

Root Privilege Protection: Why This Vulnerability Strikes Differently 

Most software vulnerabilities force attackers to use several exploits: one to get in, another to gain more permissions, and a third to move through the network. CVE-2026-20245 removes those steps. An attacker who exploits this Cisco Software Zero-Day gains root-level access immediately, without needing to go through additional layers of the network. 

For example, a regional hospital network using Cisco Catalyst SD-WAN across fifteen campuses could be at risk. An attacker in another country could use this flaw to quickly change routing tables, intercept unencrypted data from medical devices, or disable the VPN connections between emergency departments and central pharmacy systems. The impact goes beyond IT and can affect operating rooms and intensive care units. 

The same risk applies to financial services. A mid-sized regional bank using Catalyst SD-WAN to connect its branch offices to the main banking platform could have transaction data and authentication credentials exposed if an attacker gains root access on an edge router. 

Command Injection Defense: What Administrators Must Do Right Now 

Cisco has not yet released an official software patch. This is the difficult situation administrators are dealing with. In the meantime, Cisco’s advisory outlines specific command-injection defense steps that can reduce, but not fully eliminate, the attack surface while engineering teams work on a permanent fix. 

Restrict Management Interface Access Immediately 

The best immediate step is to isolate the SD-WAN Manager web interface from untrusted networks. Administrators should configure access control lists (ACLs) to allow management traffic only from known, authorized IP addresses. If there is no need to access the management interface from the public internet, which is almost always the case, that access should be blocked at the perimeter firewall. 

Enable Out-of-Band Management Where Possible 

Edge device hardening starts by separating management traffic from data traffic. Organizations that use a dedicated out-of-band management network for SD-WAN Manager access greatly reduce their risk. If an attacker cannot reach the management interface, they cannot exploit the vulnerability, no matter how serious it is. 

Audit Active Sessions and Review Logs for Anomalous Commands 

Since exploitation may already be happening in some environments, reviewing logs is essential. Security teams should check SD-WAN Manager logs for unexpected API calls, strange command sequences, or authentication events from unknown IP addresses. Cisco’s Talos threat intelligence unit has published specific indicators of compromise (IoCs) that administrators should compare with their SIEM data right away. 

Deploy Inline Intrusion Prevention Signatures 

Cisco’s IPS signature database and third-party systems from vendors such as Palo Alto Networks and Fortinet have begun releasing detection signatures for the specific HTTP request patterns associated with CVE-2026-20245. Enabling these signatures on any inline security device before the SD-WAN Manager interface adds an important detection and blocking layer while the permanent patch is being developed. 

Edge Device Hardening: The Wider Lesson 

The Cisco Catalyst SD-WAN vulnerability remediation and protective mitigation guide, which runs to several pages, but its underlying philosophy can be summarized in a principle that enterprise security architects have long preached and organizations have long deferred: reduce the attack surface of management-plane interfaces as aggressively as possible, at all times, not just during active zero-day events. 

Edge device hardening is not a one-time project; it is an ongoing approach. Devices at the edge of corporate networks, such as SD-WAN routers, firewalls, and load balancers, always handle traffic from the public internet. This constant exposure makes them key targets. Organizations that have already set up strict ACLs, multi-factor authentication for management access, and network segmentation are finding this week’s advisory to be a minor issue. Those who delayed these controls are facing a crisis. 

The Center for Internet Security (CIS) benchmarks, NIST SP 800-189 guidance on routing security, and Cisco’s own hardening guides have all recommended these controls for years. CVE-2026-20245 does not bring new advice. Instead, it enforces long-standing best practices with real consequences. 

The Patch Timeline and What Comes Next 

Cisco has said that software fixes for CVE-2026-20245 are being developed and will be released through the usual advisory update process. Organizations should monitor Cisco’s Security Advisory page at cisco.com/go/psirt for patch availability by version and apply updates immediately upon release, in accordance with their patching SLAs. 

The wider cybersecurity community sees this event as part of a bigger trend. SD-WAN platforms are now major targets because they hold a key position in enterprise networks—they are trusted, authoritative, and often not monitored as closely as endpoint devices. The Root Privilege Protection gap shown by CVE-2026-20245 is not unique to Cisco; similar issues exist in platforms from VMware, Fortinet, and others. 

The difference between organizations that get through zero-day events and those that suffer major breaches usually lies less in how advanced their response is after the advisory is released. It is how strong their defenses were before the event. Teams that had already secured management access, set up strong logging, and used inline detection are now seeing ‘being blocked’ as a sign of success, not a last-minute emergency. 

The zero-day risk will end when the patch is released. The work to harden systems should have started well before the vulnerability appeared.

Source: Cisco Security Advisories 

Armonk, New York  

Last year, hackers exploited known software vulnerabilities to steal about $4.5 billion from American businesses. In the process, they exposed tens of millions of social security numbers, credit card numbers, and billing histories. On average, it takes companies 60 days to fix a discovered flaw. Criminal networks use that two-month gap to their advantage. 

IBM and Red Hat want to close that gap for good. 

The Project Lightwell Vault: What IBM Is Actually Building 

Project Lightwell Vault defends corporate files by taking a new approach: it puts a large team of engineers directly into the software supply chain. The IBM Security Initiative, announced at the company’s headquarters in Armonk, New York, comes with a $5 billion investment and involves 20,000 engineers. That’s about as many people as work in a mid-sized American city. These engineers focus solely on identifying, verifying, and fixing weaknesses in open-source code before they reach a company’s systems. 

This isn’t just a firewall upgrade or a new antivirus subscription. IBM is building what it calls a centralized security clearinghouse for enterprise open-source software. This idea directly affects every CFO, CTO, and chief risk officer at companies that use cloud infrastructure. 

Why Open Source Became the Soft Underbelly of Enterprise IT 

About 90 percent of today’s commercial software uses open-source parts. The Linux kernel, Apache web server, and OpenSSL encryption library are examples. These tools are the hidden foundation of the internet, but many are maintained by volunteers who often don’t have formal security review processes. 

When a researcher finds a serious flaw in one of these components, a Common Vulnerabilities and Exposures (CVE) alert is made public. Unfortunately, this alert also reveals the weakness to hackers. Companies then rush to fix the problem, but often release patches weeks or months after criminals have already begun exploiting it. 

Red Hat Engineering identified this structural problem years ago. The company’s enterprise Linux distribution, RHEL, has long maintained backported patches security fixes extracted from the latest upstream code and surgically reapplied to older, stable versions running in production environments. The technique allows a bank running a three-year-old server configuration to receive a critical security update without rebuilding its entire software stack. Open Source Backporting, as it is formally known, is the operational backbone of the IBM Red Hat Project Lightwell enterprise open-source security architecture. 

The 20,000-Engineer Machine and How It Runs 

Red Hat Engineering brings unmatched open-source expertise to the corporate world. With Project Lightwell, their engineers do more than just scan for known problems. They carefully review source code, identify production vulnerabilities before they become public, create tested patches, and apply these fixes directly to live business systems. 

The automation part is what sets the IBM Security Initiative apart from what most companies can do on their own. IBM has built a continuous integration pipeline, similar to an assembly line for security patches. This system tests each fix on many different business setups before it goes live. If a patch works on a standard Red Hat system but causes problems for a custom database at an insurance company, it won’t be sent to that company. Instead, the system signals the issue and sends it to a person for review. 

This degree of detail is very important. Many companies put off applying known fixes because they worry about interrupting their operations. A 2024 Ponemon Institute study found that 57 percent of IT managers had delayed patching a critical fault because they feared downtime. Project Lightwell Vault does this by providing pre-tested, environment-specific fixes that require little additional checking before use. 

What Production Vulnerabilities Actually Cost American Businesses 

Take a mid-sized regional retailer that uses an e-commerce platform built with open-source components. This is common for thousands of American companies. If a new vulnerability emerges in a popular authentication tool, the retailer’s IT team might have only a few engineers to assess, test, and install the patch. While this process takes weeks, the company stays at risk. 

Multiply that scenario across the Fortune 500 and the small- to midsize enterprises that supply them. The IBM Red Hat Project Lightwell enterprise open-source security architecture is designed to collapse that exposure window from weeks to hours by performing evaluation and backporting work centrally and at scale, and by delivering a verified fix directly to the customer’s environment. 

The customer’s network keeps running. Their engineers can focus on other tasks. And a backdoor that hackers could have used on Tuesday is closed by Wednesday morning. 

The Wider Signal IBM Is Sending to the Market 

A $5 billion investment is much more than a research grant. It’s a major bet on the market. IBM is showing that enterprise security, especially the tough work of maintaining open-source software at scale, is important enough to deserve the same kind of investment as a big hospital or a highway project. 

For executives looking at their own security, Project Lightwell Vault raises an important question. If IBM is spending five billion dollars to fix a problem your team handles with just a few engineers and quarterly patches, what does that say about your current approach? 

The answer is becoming clear: protecting corporate files from today’s fast-moving threats needs the kind of Red Hat Engineering expertise and automation that most companies can’t build on their own. IBM is betting that businesses will pay for centralized access to this service, and with breach costs rising, the numbers seem to support their bet. 

The true test of Project Lightwell won’t be in press releases, but in breach statistics over the next few years. If the clearinghouse model works, the 60-day window for hackers will get smaller. That means American shoppers’ Social Security numbers will be a bit safer on the servers that store them.

Source: IBM Newsroom 

Mountain View, California 

Even a single unnoticed vulnerability on a smartphone can put far more than the device at risk. It can reveal banking credentials, private photographs, corporate emails, authentication tokens, and years of personal conversations. That reality explains why security researchers paid close attention when Google Just Fixed 124 separate Android Software Bugs in its June 2026 security update, including a serious flaw that could have let attackers gain extra privileges on a device without any action from the user. 

For billions of Android users around the world, this update is more than just routine maintenance. It’s a sign that our smartphones now hold our personal identities, financial information, and work communications. Even one missed weakness can lead to serious risks. 

Why Google Just Fixed Android Software Bugs Before Attackers Could Exploit Them 

The most important issue fixed in this update is called CVE-2025-48595. It’s a serious vulnerability found in Android’s system framework. Security experts say it’s a privilege escalation flaw, meaning malicious software could gain more permissions than it should. 

Most mobile threats need users to click on untrustworthy links or install risky apps. This vulnerability is different because attackers could exploit it directly on the device, without needing the user to do anything after the initial breach. 

This difference is important. 

Imagine if someone steals a password or if you download an innocent-looking app from an unofficial source. In some cases, an attacker could exploit this vulnerability to gain greater control over the device’s operating system. Once they have that control, harmful code could access protected data, tamper with security settings, or hide itself in ways that are hard for users to detect. 

Google responded by quickly releasing a thorough fix for the privilege escalation fix before attackers could take advantage of it. 

The June Security Patch Addresses More Than One Critical Threat 

The June update covers much more than just one vulnerability. 

This latest June Security Patch resolves 124 vulnerabilities across multiple Android components, including the framework, system services, kernel modules, and hardware-specific software from device makers. 

Security teams often compare maintaining Android security to fixing a big city’s infrastructure. One broken bridge might get attention, but many smaller problems together can still cause major risks if they aren’t fixed. 

This month’s update tackles vulnerabilities affecting: 

  • Android Framework components 
  • System services 
  • Kernel subsystems 
  • Media processing functions 
  • Hardware abstraction layers 
  • Vendor-specific software implementations 

The size of this update shows how seriously Google is working to protect Android from an increasing number of threats. 

Now that smartphones are used as digital wallets, security keys, and work devices, each security update matters more than ever before. 

Understanding the Local Execution Threat Behind CVE-2025-48595 

The term Local Execution Threat might sound technical, but what it means is actually simple. 

A local execution attack usually means harmful code is already on the device before it’s used to exploit a weakness. Once it’s there, the attacker tries to use flaws in the operating system to get more control. 

In the past, cybercriminals have regularly combined several vulnerabilities. One lets them in, another gives them more privileges, and a third helps them stay hidden. 

This step-by-step method is why vulnerabilities like CVE-2025-48595 are especially worrying. 

Security researchers often warn that attackers don’t just use one exploit. Instead, they combine several weaknesses to create complex attacks that can get around defenses. 

Google’s Privilege Escalation Fix disrupts one of those potential links. 

By closing off this escalation path, Google makes it much less likely that small breaches might turn into full device takeovers. 

System-Level Protection Becomes Increasingly Important 

Modern Android security is built on keeping different parts of the system separate. 

Apps run within limited spaces; permissions control what they can access; and several checks help prevent unauthorized operations. These protections only work well if the boundaries between system parts stay strong. 

The June update makes system-level protection stronger by fortifying these boundaries. 

If vulnerabilities show up in the system framework, they can break down the barriers that keep trusted and untrusted processes apart. Attackers look for these weaknesses because they let them get around normal security rules. 

For businesses, the risks are even greater. 

If a smartphone connected to company emails, customer databases, or cloud tools is compromised, it can open the door to bigger security problems for the whole organization. That’s why businesses closely monitor Android security alerts and often rush to install important updates. 

The newest system-level protections help lower these risks and keep Android’s overall security strong. 

What the Google Android Security Update Patch Notes June Vulnerability Remediation Framework Discloses 

Security experts pay attention not just to each vulnerability, but also to how companies respond to them. 

The Google Android security update patch notes and the June vulnerability remediation framework provide insight into Google’s broader defensive strategy. Rather than addressing isolated flaws, the company keeps refining a structured remediation process that identifies, evaluates, prioritizes, and resolves vulnerabilities across the Android ecosystem. 

This process is more important than ever because Android runs on thousands of device models from many different manufacturers. 

Unlike systems with strict hardware control, Android updates have to go through several steps. Google creates the fixes, chipset makers adjust them, phone manufacturers add them to their devices, and wireless carriers usually check them again before sending them out. 

The June patch notes and Google’s security process show that working together is now essential for protecting users at scale. 

Without this teamwork, even the best fixes could take months to reach users. 

Why Carriers and Manufacturers Face Immediate Pressure 

Google can release a patch, but that’s just the first step. 

Now, wireless carriers, phone makers, and business service providers need to roll out the update to all their supported devices as quickly as possible. 

The rush comes from a basic cybersecurity rule: once a vulnerability is made public, attackers start looking for ways to use it. 

Security researchers, ethical hackers, and cybercriminals all study public advisories to see how flaws work. If updates are delayed, attackers have more time to exploit devices that haven’t been patched. 

That’s why big manufacturers are under pressure to speed up updates and make sure users get the latest protections quickly. 

For users, the best way to stay safe is simple: install updates immediately as they’re available. 

The Larger Message Behind Google’s Security Push 

The June 2026 update shows that this issue goes beyond just Android. Smartphones are now our ID cards, wallets, health trackers, communication tools, and work devices. Keeping them safe takes persistent attention. 

Google fixing over a hundred Android software bugs in one update shows how complex today’s operating systems are and why periodic security work is so important. The mix of a top-priority privilege-escalation fix, stronger system-level protection, a fix for a serious local execution threat, and the broad June patch all show that Google is focused on preventing problems, not just reacting to them. 

As attackers continue to look for new weaknesses, the effectiveness of the Google Android security update patch notes and the June vulnerability remediation framework may prove just as important as any single patch. The battle between defenders and cybercriminals never really ends it just moves on to the next vulnerability, the next update, and the continuous effort to keep billions of devices safe.

Source: Android Security  

Redmond, Washington 

Your laptop fan kicks on, a browser tab freezes mid-presentation, and the spinning cursor becomes the most hated icon on your screen. For the roughly 400 million active Windows 11 users in the United States alone, the moment of system stall is not an abstraction it is a recurring tax on productivity. Microsoft’s answer arrives this month in the form of a sweeping release that upgrades spark renewed performance expectations from living rooms to C-suites: the June Feature Drop for Windows 11. 

This update goes beyond being a new look. It focuses on local hardware, better management of connected devices, and stronger system dependability. Microsoft has been building these improvements since it started the Copilot+ PC initiative. 

How June Feature Drop Upgrades Spark a New Era for Windows 11 

The June Feature Drop comes at an important time. In the past year and a half, Intel, Qualcomm, and AMD have released chips with built-in Neural Processing Units. Until now, most Windows users couldn’t tell if these chips were being used or just sitting idle. This update finally gives users that insight. 

Microsoft is adding NPU Resource Metrics right into Task Manager, the tool many people use when their computer slows down. This new feature shows real-time usage, memory bandwidth, and which processes are using the NPU. Now, a software developer in Austin can see the same detailed hardware data that a chip engineer might get from special tools. 

This matters for more than just curiosity. When you use AI features like live captions, background blur in video calls, or image enhancement in Photos, the NPU handles the work instead of the CPU or a remote server. With NPU Resource Metrics, power users can see exactly how this happens and spot any slowdowns, all without extra monitoring tools or confusing performance data. 

Shared Audio Settings: The Peripheral Problem Microsoft Finally Fixed 

If you’ve ever switched between a Bluetooth headset, a conference speakerphone, and a USB DAC on your Windows computer, you know the hassle. Each app keeps its own audio settings, so changing devices regularly means going through Settings, then the app, and back again. 

Shared Audio Settings fixes this problem. The new system lets you set your preferred audio input and output for the whole computer, and apps will use those settings by default. You can still change settings for individual apps if needed. Now, someone using a Bloomberg terminal, Zoom, and a media player at the same time doesn’t have to set up audio for each one every day. 

For the 33 million small businesses in the United States, many without dedicated IT staff, Shared Audio Settings are a quiet but important improvement. These changes may not make headlines, but over time, they noticeably boost productivity. 

The Microsoft Windows 11 June cumulative feature update installation manual documents this audio architecture in detail, including registry-level switches for enterprise administrators who need to enforce specific peripheral policies across managed device fleets. 

Desktop Responsiveness: The Engineering Behind Fewer Frozen Apps 

This update also improves Desktop Responsiveness through fixing a problem Windows engineers call “ghost window” behavior. This happens when an app keeps running, but its display freezes, leaving you looking at a screen that doesn’t respond. 

The fix involves two major changes to the system. First, it ensures that the parts of programs that control the display receive sufficient CPU time, even when background tasks such as virus scans or cloud syncs are running. Second, Microsoft has reduced the time it takes for Windows to display a recovery prompt, so users get help faster rather than waiting through a long freeze. 

In real life, a graphic designer using Adobe apps with a large cloud library should experience fewer freezes while working. A high school student turning in a paper online while Windows updates run in the background will notice less lag and fewer sudden slowdowns. 

These changes aren’t flashy, but they show the careful work that makes an operating system reliable and trustworthy, instead of just something people put up with. 

What the Microsoft Windows 11 June Cumulative Feature Update Installation Manual Covers 

Deployment matters as much as the features themselves. The Microsoft Windows 11 June cumulative feature update installation manual outlines staged rollout procedures, compatibility tests for devices running older NPU firmware, and Group Policy settings for enforcing Shared Audio Settings in managed environments. 

IT administrators at mid-sized companies, with 50 to 500 users, will find the manual’s section on NPU Resource Metrics especially helpful. Microsoft now lets admins send NPU usage data to Windows Admin Center, so they can see how AI features are used across all their devices. 

Home users who receive updates automatically will receive the June Feature Drop through Windows Update, as long as their computers meet the Trusted Platform Module requirements in place since Windows 11 launched. 

The Larger Shift This Update Represents 

Bringing together NPU Resource Metrics, Shared Audio Settings, and improved Desktop Responsiveness in a single update shows Microsoft’s clear strategy. The company believes that local hardware, not just cloud services, will power the next generation of personalized computing, and it is updating Windows 11 to match that trend. 

This shift changes how American workers, students, and creators connect with their computers. When your laptop shows you how its AI chip is working and lets you easily control your devices, it no longer feels mysterious. These upgrades make using your computer feel more like working with professional tools than the basic consumer devices of the past. 

Microsoft’s June update doesn’t fix every problem in Windows, but it helps make the operating system more trustworthy and better suited for today’s hardware, not just the systems of the past.

Source: Microsoft Source 

Cupertino, California  

Most apps are forgotten within three days of being downloaded. While the average American has 80 apps on their iPhone, they use fewer than nine regularly. Amid all this digital clutter, Apple announced the winners of the Apple Design Awards 2026, honoring 12 outstanding apps and games that demonstrate innovation, artistry, and technical achievement. These awards are not just for showing up. They are Apple’s way of indicating the direction it wants software to take. 

The timing is deliberate. The awards were unveiled ahead of the Worldwide Developers Conference, which begins June 8. Every developer with an Xcode project open right now is paying attention. 

What Apple Handed The World’s Best App Creators — And Why It Matters 

Winners were selected from 36 global finalists. One app and one game were recognized across six categories: Delight and Fun, Inclusivity, Innovation, Interaction, Social Impact, and Visuals and Graphics. The selection process is not a popularity contest. Apple’s internal teams evaluate on criteria that include how well an app uses platform-native technologies, how cleanly the experience is architected, and whether the interaction design solves a real problem with genuine elegance. 

The Apple Design Awards 2026 winners represent teams from the Netherlands, Spain, India, the United Kingdom, the United States, Italy, Canada, and Poland  a geographic spread that reflects how decentralized serious mobile innovation has become. The next breakthrough iPhone experience is as likely to come from a two-person studio in Amsterdam as from a well-funded startup in San Francisco. 

Susan Prescott, Apple’s vice president of Worldwide Developer Relations, made the stakes plain. “Whether delivering intuitive features or exciting gameplay, these apps and games represent the very best of what our platform makes possible.” 

The Quiet Masterpiece: How “grug” Wins By Doing Less 

The most interesting winner this year is not the most eye-catching. It’s a small app called grug, made by Ocho, a studio in the Netherlands. It won the Delight and Fun category, and anyone who builds software should take a closer look. 

Grug shares daily wisdom using simple, Neolithic grunts. Reading statements like “only walking grug find breakthrough … sitting grug find nothing” is described as a basic joy. What clearly stands out is its scribbled design—a clever and simple approach that doesn’t take itself too seriously. 

That description encapsulates something important about interaction design at the highest level. Grug does not have a dashboard. It does not have a feed, a settings page with 30 toggles, or a subscription upsell screen that appears on day three. It has one idea, executed with enough personality and restraint that users come back for it daily. The Apple Design Award winners’ technical implementation and user interface design log for this category specifically rewards experiences that feel “memorable, engaging, and satisfying” — and Grug achieves all three, lacking complex layouts or feature bloat. 

This is the lesson that most product teams ignore: simplicity is not the lack of effort. It is the result of extraordinary editorial discipline. 

Visual Artistry at Scale: Cyberpunk and the Mac Moment 

At the other end of the production scale, Cyberpunk 2077: Ultimate Edition by CD Projekt S.A. won the award for Visuals and Graphics. The fact that such an ambitious game now runs on Apple Silicon well enough to win a design award—based on quality, not just novelty—shows that Mac gaming is changing in a big way. 

Visual artistry is more than just decoration. When a game can show that much detail and complex lighting on a regular laptop, it changes what developers think is possible on the Mac. Expectations rise, and the limits move higher. 

Mobile Innovation on Vision Pro: The NBA’s Bet on Spatial Sports 

The Innovation category showed how Apple uses these awards to highlight new platform features. The NBA: Live Games & Scores app by NBA Media Ventures won for its Apple Vision Pro experience. It lets fans watch up to five live games at once, follow real-time stats with floating leaderboards, see player movement on a 3D court, and use Spatial Audio. 

Sports is the clear winning use case for spatial computing. While headsets can feel awkward for work or social media, they make perfect sense when you want to watch a live game with extra stats, different camera angles, and an overhead court view all at once. Upon recognizing this app, Apple is showing that mobile innovation in 2026 goes beyond just what happens on a phone screen. 

Inclusivity as Design Standard, Not Afterthought 

Guitar Wiz by Bijoy Thangaraj, an individual developer based in India, won the Inclusivity award for its all-in-one toolkit that provides spoken instructions on everything from pitch to finger positioning, supporting all musicians by leveraging Apple technologies, including Dynamic Type, Increased Contrast, and Differentiate Without Color. 

A solo developer beat teams with big budgets and marketing departments by building for everyone. This result should change how studios view accessibility. It is not simply a box to check. When done well, it becomes a real advantage—and it’s clear Apple is looking for this kind of work. 

What the 2026 Class Tells Developers About Tomorrow 

The Apple Design Awards 2026 are always partly retrospective  celebrating what was shipped — and partly prescient, signaling what Apple will reward next. This year’s class sends three clear signals to every app creator paying attention. 

First, restraint wins. grug proves it. The Apple Design Award winners technical implementation and user interface design log for Delight and Fun does not go to a complex product, but to one that is focused. 

Second, spatial computing needs builders. The NBA app’s Innovation win is Apple inviting the wider developer community to take VisionOS seriously as a media platform, not just an experiment. 

Third, accessibility is a mark of quality. Guitar Wiz did not win just because it was accessible. It won because it was built so well, plain and simple. 

The winning developers are from teams around the world, and their work demonstrates innovation, artistry, and technical skill in app and game design. What Apple gave these twelve app creators represents more than merely a trophy. It is a public benchmark that will influence what the next generation of iPhone software looks like, even if most users never know these apps by name. 

Source: Apple reveals winners of ‍‍‍the 2026 Apple Design Awards 

Washington, District of Columbia  

The top executive in the semiconductor industry has been called to Capitol Hill, and he can expect some tough questions. 

Senator Elizabeth Warren, the top Democrat on the Senate Banking Committee, formally invited Nvidia Chief Jensen Huang to appear before the committee on June 11 and set a Monday deadline for him to confirm his appearance. Her letter made the stakes clear: Huang would have a chance to explain “NVIDIA’s views on U.S. export control laws and regulations and NVIDIA’s business in China.” In other words, Washington wants to know if the world’s most valuable chip company has been following the rules. 

Tech investors and policy watchers have seen this moment coming for months. 

NVIDIA Chief Jensen Huang Must Now Face Washington’s Sharpest Questions 

Huang’s schedule over the past six weeks has been dramatic. He traveled with President Donald Trump to Beijing in mid-May for a major summit with Chinese President Xi Jinping. He was photographed outside the Great Hall of the People. Then, a few weeks later, he received a Senate invitation. These public appearances are intentional and meant to send a message. 

Warren’s concerns are based on a specific and troubling body of evidence. The Department of Justice has brought multiple criminal enforcement actions alleging the unlawful diversion of Nvidia’s most advanced processors to China. Those cases allege schemes involving millions of dollars in graphics processing units routed to China through Malaysia and Thailand; exports and attempted exports of $160 million in H100 and H200 chips; and $510 million in diverted servers, connected to a March 2026 indictment involving individuals linked to Super Micro Computer. 

That last number half a billion dollars in allegedly diverted servers shows a major breakdown in the global supply chain. It also goes against what Huang has said publicly: that there is no evidence of significant AI chip diversion and that Nvidia’s market share in China has basically dropped to zero. 

Warren’s letter says these criminal allegations do not match the CEO’s public statements, putting more pressure on Nvidia’s compliance practices. The senator wants to know who knew what, and when. 

What the Senate Banking Committee Is Really After 

The June 11 hearing is about more than just one company’s sales figures. The United States Senate Banking Committee’s Nvidia CEO official testimony hearing schedule constitutes a broader inflection point in how Washington views artificial intelligence infrastructure and its connection to national security. 

NVIDIA’s advanced chips run data centers and AI systems in many industries, putting the company at the center of the global AI boom and making it a key focus in Washington’s debate over export controls. When senators say they are concerned about chips helping China’s military, they mean it literally. Warren put it simply on CNBC’s Squawk Box: “In China, these are chips that are actually used for military purposes.” 

The committee’s questions go beyond national security. Warren also asked Nvidia’s audit committee whether it views the alleged illegal diversion of Nvidia products as a serious legal or regulatory risk and whether it has conducted any independent review of its export-control compliance programs. These questions can affect stock prices and lead to shareholder lawsuits, and Nvidia’s legal team is aware of that. NVDA shares fell about 1% in after-hours trading when the invitation became public. 

Export Control Laws at a Breaking Point 

Export controls on advanced semiconductors have faced major challenges since August 2022, when the U.S. government first put strict limits on shipping A100 and H100 chips to China. Since then, each new Nvidia product has led to more regulatory changes and enforcement issues. 

If the DOJ allegations are true, the evidence that these controls are being bypassed indicates a broader problem that no single company can explain on its own. Chips do not move through global supply chains in places like Malaysia, Thailand, and Singapore without help from intermediaries, freight companies, and shell businesses. The Senate Banking Committee wants to know if Nvidia’s internal compliance was strong enough to catch and stop this diversion, and whether company leaders truly did not know or chose not to look too closely. 

IDC data from April 2026 showed Nvidia’s share of China’s AI accelerator card market fell from about 95% to around 55% in 2025, while Huawei led domestic chips with about 20%. Huang has admitted that Nvidia has “essentially ceded the Chinese AI market to Huawei.” This pullback, no matter the reason, has not ended the compliance questions. In fact, losing revenue can create new risks. 

Why Artificial Intelligence Infrastructure Is the New Geopolitical Battleground 

It would be a mistake to read this hearing as a routine oversight exercise. The United States Senate Banking Committee Nvidia CEO official testimony hearing schedule sits at the intersection of three forces that rarely converge so visibly: national security, capital markets, and the global architecture of artificial intelligence infrastructure. 

The Senate’s investigation is similar to a separate probe started by Republicans on the House Energy and Commerce Committee. This shows that AI chip export controls are one of the few issues both parties agree on, even if they disagree on the details. When both Senate Democrats and House Republicans want an investigation, regulation usually follows. 

For American executives in the semiconductor and software industries, this hearing will set a new standard. The days when tech CEOs could treat Washington as a distant concern, handled with lobbying or occasional testimony, are over. NVIDIA Chief Jensen Huang created one of the most important hardware platforms within modern computing, and now it is at the center of a global political struggle with no easy answers. 

The Bigger Picture Behind the Invitation 

The bigger message from the June 11 hearing is that the federal government plans to play a bigger and ongoing role in how America’s top tech companies sell products overseas. Export control laws will get stricter, enforcement will increase, and compliance will become more expensive. Companies that see these laws as just a formality rather than a real business risk could end up like Nvidia defending their choices before a skeptical Senate committee while the markets watch. 

Huang has not yet said whether he will testify now or send someone else. The deadline has passed, and Washington is waiting. No matter what he decides, the questions will remain. 

The era of chip companies avoiding accountability now has a date: June 11, 2026.

Source: Warren Calls on NVIDIA President & CEO Jensen Huang to Testify at Upcoming Committee Hearing on AI and the American Dream

Redmond, Washington 

Your inbox contains 340 unread messages. Three calendar appointments overlap with a board presentation you still need to start. A vendor contract is lost in a SharePoint folder you last opened eight months ago. You spend forty minutes searching for it. This isn’t just a productivity issue. It’s a deeper problem with how enterprise software has always worked: it reacts to you instead of anticipating your needs. 

Microsoft just changed that equation. 

The Microsoft Work IQ Tool Is Not Another Chatbot 

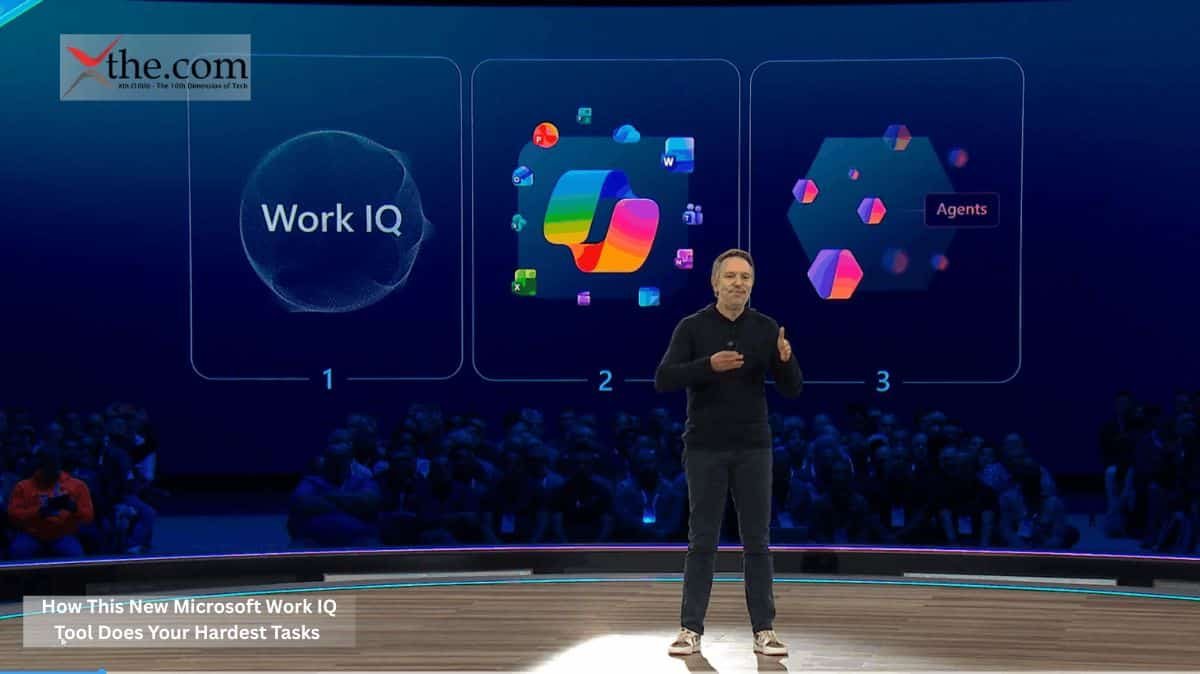
Released last month with new developer documentation, the Microsoft Work IQ Tool works on a different level than anything Microsoft has offered before. It’s not a chatbot you interact with. Instead, it acts as an intelligence layer: a real-time reasoning engine built into Microsoft 365 Context that constantly creates and updates a living map of your organization’s activity. 

It’s better to see it as institutional memory that can also take action, rather than just another feature. 

The engine gathers information from across Microsoft 365, including meeting schedules, email threads, shared files, document changes, and even details about who works together and how often. Using this data, it builds what Microsoft calls a “contextual activity graph,” which is a dynamic picture of how work really happens, not just how org charts or project coordination tools show it. 

How Work IQ APIs Connect External Tools to Live Organizational Data 

The most important part of this launch isn’t the engine itself. It’s the Work IQ APIs, tools for developers that let external applications access and use the contextual graph. 

In the past, enterprise automation has often been fragile. For example, a script that files expense reports may work until someone renames a folder, changes an approval process, or adds a new signatory. When that happens, the automation fails, and someone has to fix it. This cycle has wasted a lot of companies’ time. 

Work IQ APIs break that pattern through Semantic Indexing, which means the system understands the meaning of files, emails, and calendar events rather than just their location or label. An external scheduling tool, for instance, can ask the API not simply “when is Sarah free?” but “when is Sarah free and not in a strategic planning window, given that her team has a product review cycle that ends Friday?” The API returns an answer grounded in a real organizational context, not just raw calendar availability. 

Semantic Indexing: Why It Matters More Than Search 

Standard enterprise search relies on keywords. If you type “Q3 vendor contract,” the system shows every document with those words, usually sorted by how recent they are. Semantic Indexing in the Microsoft Work IQ Tool works differently. It reads documents for their main ideas and maps how they relate to each other, such as linking a contract to the preceding email conversation, the procurement officer who approved it, and the renewal date hidden in paragraph nine of an attachment. 

This understanding of relationships lets Automated Workflows go beyond simple, one-step actions. For example, an agent using Work IQ APIs could track when a contract is about to expire, draft a renewal memo in the original author’s style, send it to the appropriate approver based on the current organization, and schedule a follow-up meeting. All of this can happen without a person giving detailed instructions for each step. 

Microsoft’s documentation refers to these as “compound task sequences.” They are a major shift away from traditional robotic process automation. 

Automated Workflows and the Shift to Self-Directed Systems 

Executives and operations leaders should pay close attention to what Automated Workflows can mean for their organizations. For example, an accounts payable team at a mid-size company handles hundreds of invoices each month. Each invoice needs to be matched with a purchase order, delivery confirmed, sent to the budget owner, and recorded. Mistakes can happen at any step. 

An agent using Work IQ APIs and Microsoft 365 Context, such as purchase orders, delivery confirmations from emails, and budget data from org charts, could handle this process with little human help. It would only flag exceptions that don’t fit the usual rules. 

This is not hypothetical. Microsoft’s developer documentation includes reference implementations for exactly this class of workflow. 

The Microsoft Work IQ API Enterprise Integration and Data Security Configuration Guide: What Organizations Must Address 

Any real discussion of this system must address the concerns covered in the Microsoft Work IQ API enterprise integration and data security configuration guide. When an intelligence engine can always read emails, files, and calendars across an organization, a misconfiguration can have serious consequences. 

The documentation describes detailed permission controls. This means an outside application using Work IQ APIs can be limited to certain users, data types, or time periods. Data residency controls match Microsoft 365’s existing compliance settings, and all API activity is tracked in the same audit records that compliance teams already use. 

The security design is solid. However, it’s up to each organization to set it up correctly. Success depends on thorough implementation, not just the platform itself. 

What This Means for the People Doing the Work 

The Microsoft Work IQ Tool doesn’t take away jobs. Instead, it removes the hardest tasks that feel like work but don’t require real thinking, such as searching through calendars, hunting for documents, and sorting emails. These activities take up about forty percent of a knowledge worker’s day, according to a 2023 McKinsey Global Institute analysis. 

This raises a new question: when routine office work takes less time, what will organizations expect of employees with more time? The answer will shape the future of enterprise productivity, and Microsoft has shown with this new system that it wants to lead that change. 

The infrastructure is already running. The Work IQ APIs are fully documented and ready to use. Organizations that start using Microsoft 365 Context connection early won’t just automate faster they’ll gain a growing advantage over those still searching for contracts within forgotten folders.

Source: Announcing the new Work IQ APIs