The new patent application shows that Apple is increasing its research into advanced AI chip development, which will transform how future American devices manage AI processing tasks. The United States Patent and Trademark Office received the patent application, which describes architectural advancements that will enhance on-device AI capabilities, energy usage, and system integration.  

Patents function as effective indicators of a company’s future plans, even though they rarely lead to actual commercial products. The filing demonstrates that Apple wants to establish local AI processing as a vital feature that distinguishes its hardware ecosystem from competitors.  

A New Direction for AI Chip Architecture  

The patent focuses on specialized AI processing units that exceed the machine-learning capabilities of traditional CPUs and GPUs. The designs build on Apple’s existing neural engine architecture by introducing new processing methods that will improve performance and reduce energy consumption.  

Apple’s approach reflects a broader industry trend toward dedicated AI hardware, which uses specialized components to perform tasks such as image recognition, natural language processing, and predictive analytics.  

The shift becomes essential because AI workloads require higher processing power, operating at faster speeds with better energy efficiency.  

On-Device AI as a Strategic Priority  

The patent’s main focus shows the importance of AI systems that operate on the user’s device. The system achieves faster response times and stronger user privacy protection by processing data directly on the device rather than using cloud systems.  

Apple has used on-device processing as its main strategic element since its inception because this patent strengthens that approach. The system allows users to run advanced AI models directly on their devices, resulting in faster performance and reduced ongoing internet access requirements.  

The system provides users with an experience that becomes more responsive and secure when they use applications that manage confidential information.  

Performance Gains and Efficiency Improvements  

The proposed chip designs aim to optimize performance across a range of AI tasks. Apple’s use of specialized processing units enables better workload distribution, which helps all components achieve their maximum operational capacity.  

The system delivers performance improvements and energy efficiency gains, enabling devices to run demanding AI computations while maintaining battery life.  

Power consumption and thermal management are critical factors Apple must consider when developing its portable devices, which require efficient operation.  

Impact on Device Design and Capabilities  

The development of AI chip technology directly affects the design of electronic devices, as more efficient chips enable thinner, lighter devices that extend battery life and enable advanced features.  

The patent suggests that future devices could incorporate enhanced AI capabilities without increasing size or weight. The system enables users to perform real-time environmental assessment together with customized experiences and enhanced automated processes.  

Apple leverages its hardware and software integration to capitalize on these technological advancements.  

Pricing and Market Positioning  

The development of AI chips will affect how companies set their pricing. The introduction of more advanced and efficient chips will increase their value, enabling manufacturers to charge premium prices for their high-end products.  

Improving product efficiency will reduce production costs over time, helping various industries adopt new technologies.  

Apple uses its control over chip design to achieve a performance-to-cost balance, enabling it to establish its market presence during the AI era.  

Ecosystem Lock-In and Competitive Advantage  

The main consequence of Apple developing its AI chip technology is a lock-in effect that keeps users in its ecosystem. Apple develops its own hardware that works best with its software, resulting in a system that keeps users in its ecosystem. The method improves user experience but restricts users who want to use different platforms.   

Apple has built its successful business model on an ecosystem strategy, which will be further strengthened by its AI chip development.  

Broader Industry Implications  

Apple has received a patent that demonstrates the current trend among technology companies to create their own artificial intelligence hardware. The technology market experiences greater innovation because companies create custom chips that enable them to execute artificial intelligence tasks.  

The development of on-device AI technology will create new design methods and usage patterns for devices, affecting all electronic devices, including smartphones, laptops, and wearables.  

Apple’s current technology improvements will set new benchmarks for performance and efficiency, shaping future industry developments.  

Challenges and Uncertainties  

The development of advanced AI chips presents benefits that require industries to overcome their existing challenges. The process involves multiple challenges, including production methods, software development, and application compatibility testing. The success of these technologies relies on their acceptance by both developers and users.  

Apple must overcome these obstacles to achieve complete success with its AI chip developments.  

From Patent to Product  

The statement proves that not every patent leads to the successful development of commercial products. However, they provide valuable insight into a company’s research and development priorities.  

The patent demonstrates that Apple is currently working on methods to improve its AI technology, which will result in upcoming products and features.  

New technological advancements will eventually become standard equipment in Apple devices once their technology reaches full development.  

Conclusion: A Shift Toward AI-Centric Devices  

Apple’s AI chip patent demonstrates an important transformation that will affect all upcoming product designs and operations. Apple has established itself as a leader in artificial intelligence computing by developing products that handle all processing activities within devices while maintaining energy efficiency and seamless system operation.  

The effects of the situation extend beyond performance; they establish new pricing structures, alter ecosystem relationships, and change how users interact with the product. The future of technology development will depend on new AI chip design innovations, which will drive changes throughout the industry.

Sources: Apple Newsroom 

Trademark classification goes agentic with USPTO’s announcement of “Class ACT” assistant
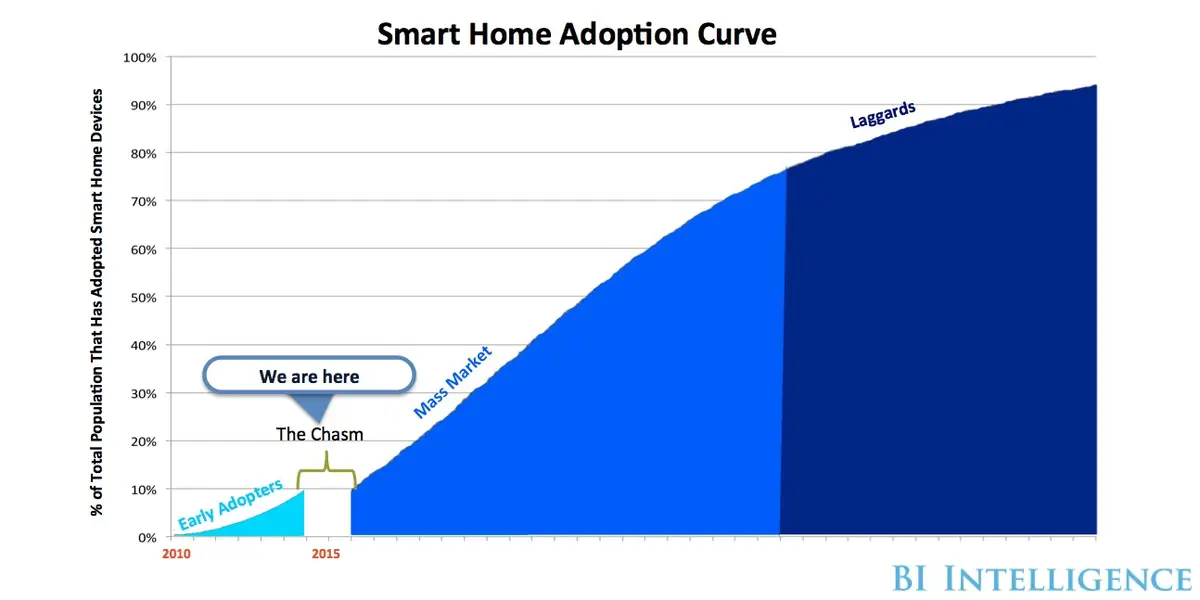
The United States is now entering a new phase of smart home technology adoption, driven by artificial intelligence. The initial development of voice-controlled lighting and thermostats has advanced to sophisticated systems capable of predictive automation, real-time monitoring, and contextual decision-making. The three leading market platforms driving this transformation are Amazon, Google, and Apple.  

The three systems provide different approaches to implementing smart home artificial intelligence, varying in system design, user security, device compatibility, and future operational efficiency. Consumers face growing difficulties when selecting a home automation system because they must understand that switching systems can lead to costly technical issues.  

The Evolution of Smart Home AI Platforms  

Smart home platforms have shifted from reactive systems to proactive environments powered by AI. Modern systems use behavior pattern analysis to automatically operate functions such as lighting, temperature control, and security protection, rather than waiting for user commands.  

Google has focused on predictive intelligence, using AI to anticipate user needs, while Amazon emphasizes broad device integration and voice-driven control. Apple, meanwhile, is prioritizing privacy and on-device AI processing.  

The divergence between these two approaches represents a major trend that requires businesses to balance three elements: convenience, intelligence, and protection of security systems.  

Amazon Alexa: Scale and Device Compatibility  

The Alexa platform, developed by Amazon, has become one of the most popular smart home systems because it offers excellent compatibility with a wide range of third-party devices.  

Alexa enables users to create automated systems ranging from basic routines to complex operations involving multiple devices. The system uses cloud computing as its primary processing method because it enables advanced functionality but also introduces delays and security risks.  

Amazon developed its system to provide users with maximum access while supporting a wide range of devices; therefore, it is ideal for people who need to use different types of equipment.  

Google Nest: Predictive Intelligence and Integration  

Google’s Nest ecosystem focuses on integrating AI with its broader data and services platform. The system provides highly personalized automation capabilities by learning user preferences over time.  

The Nest devices demonstrate their climate-control capabilities by adjusting temperature settings based on occupancy detection and recommending energy-conservation measures. Google’s strength lies in its ability to leverage data for predictive insights.  

The data-driven method raises privacy and data-use concerns, which have become crucial for consumers to consider.  

Apple Home: Privacy and On-Device AI  

The Apple smart home platform, which people connect to their Home ecosystem, takes a different approach by prioritizing privacy through its local processing system. Apple processes most of its data because its system functions without needing extensive cloud servers.  

The system delivers two benefits by eliminating the need to send sensitive data to external servers, resulting in faster response times and better protection of personal information. The Apple ecosystem works with its hardware products to deliver an uninterrupted user experience.  

The method provides excellent privacy protection, but it restricts users’ ability to connect to third-party devices, imposing more limitations than competing systems. The method provides excellent privacy protection, but it restricts users’ ability to connect to third-party devices, imposing more limitations than competing systems.  

AI Capabilities: Reactive vs Predictive Systems  

The performance of a smart home system depends heavily on its artificial intelligence capabilities. Google uses its predictive intelligence technology to analyze data and deliver automated solutions that meet user requirements before they become apparent.  

Amazon develops its AI technology to execute immediate responses when users issue voice commands or make other requests. Apple combines two different methods to create a system that understands user context while protecting their personal information.  

The decision for users is whether to choose automatic systems that operate without their input or systems that require immediate user response.  

Privacy and Data Security Considerations  

Privacy is the main reason people use smart home technology. Cloud-based systems, such as those used by Amazon and Google, require data to be transmitted and processed remotely.  

The system provides advanced capabilities, but it creates security vulnerabilities that can jeopardize user information. Apple’s local processing model reduces these risks by keeping data within the home environment.  

The growing awareness of data privacy now helps differentiate platforms.  

Cost and Long-Term Value  

The total expenses of a smart home system begin with device purchases but continue to increase through subscription fees, system limitations, and maintenance needs.  

Amazon allows users to connect multiple devices through its wide compatibility, helping them save money. Google offers advanced functions that some users will find worthwhile despite its higher price tag.  

Apple users need to pay more upfront to access the ecosystem, but they will receive lasting benefits from its integrated features and security protections.  

Ecosystem Lock-In and Flexibility  

The primary danger people face when selecting a smart home system is the risk of lock-in to its specific ecosystem. Users face high costs and difficulties when they try to switch systems after making their initial choice.  

Amazon provides its users greater flexibility by supporting a wide range of devices, whereas Apple creates a controlled ecosystem that offers seamless system integration. Google occupies a middle position between these two extremes because it provides users with both system integration and product interoperability.  

People need to understand these trade-offs because they will determine their final decision on which option to choose.  

The Future of Smart Home AI Platforms  

The smart home market will continue to develop as AI advances create more advanced automation systems and integration methods. The future will see increased adoption of hybrid models that combine local and cloud processing to deliver optimal performance and scalability.  

Amazon, Google, and Apple will dominate future development by competing to create the most effective and user-friendly solutions.  

The upcoming technological progress will make platforms more similar to one another, yet their fundamental design principles will remain different.  

Conclusion: Choosing the Right Smart Home Platform  

Selecting the right smart home AI platform requires careful consideration of compatibility, privacy, cost, and long-term value. Amazon provides businesses with a flexible solution to expand their operations, Google allows users to access its predictive capabilities, and Apple focuses on user privacy through system integration.  

Each platform has its strengths and limitations, and the best choice depends on individual needs and priorities. The ongoing development of AI technologies in smart homes makes it essential to choose solutions that create efficient, secure smart home systems with a future-ready design.

Sources: Apple Newsroom 

Google Nest

Amazon News Devices

Cybersecurity compliance is more important than ever, given the increasing sophistication and frequency of cyber threats. Cybersecurity compliance has become a key element of enterprise risk management as compliance is no longer simply a checkbox-ticking exercise. Alerts and advisories from the Cybersecurity and Infrastructure Security Agency have heightened the need for organizations to align with established compliance frameworks. 

Noncompliance or misunderstanding of the established compliance frameworks can lead to fines, sanctions, failed audits, or shutdowns for companies. Cybersecurity compliance for companies in the United States is now at the intersection of legal liability and technological resilience. 

Understanding Cybersecurity Compliance 

Cybersecurity compliance involves adhering to laws, regulations, and industry standards to protect your company’s data, systems, and networks. Compliance requirements vary by sector, but the general categories of compliance requirements are: 

  • Data security and privacy 
  • Risk management 
  • Incident detection and response 
  • Reporting and accountability 

Compliance is an evolving function, as new threats will emerge that require continual updates to the compliance framework an organization uses. 

Cybersecurity Compliance Frameworks in the United States 

The United States has a plethora of frameworks that guide organizations in their cybersecurity compliance, but the most widely accepted is the one developed by the National Institute of Standards and Technology (NIST). 

1. NIST Cybersecurity Framework (CSF) 

The NIST Cybersecurity Framework is a flexible, risk-based compliance framework with five primary functions: 

  • Identify 
  • Protect 
  • Detect 
  • Respond 
  • Recover 

The NIST CSF is widely used across many industries and serves as a baseline for an organization’s compliance preparedness. 

2. CISA Guidelines 

CISA, the Cybersecurity and Infrastructure Security Agency, produces actionable guidelines for organizations to implement in response to detected or anticipated vulnerabilities. These guidelines also alert organizations about general cybersecurity events occurring in their industry. 

3. Industry-specific Regulations 

Certain industries (such as healthcare and finance) have additional compliance requirements beyond the NIST CSF or CISA guidelines; these industries typically include stricter reporting requirements and data protection standards. 

Function Description Business Impact 
Identify Understand assets and risks Better risk visibility 
Protect Implement safeguards Reduced vulnerability 
Detect Monitor for threats Faster response 
Respond Contain incidents Minimized damage 
Recover Restore operations Business continuity 

The Compliance Lifecycle 

Cybersecurity compliance is a continuing process, not just a one-time event. The lifecycle of cybersecurity compliance involves five phases: 

1. Assessment: identifying the current state of your organization’s security. 

2. Gap analysis: determining how this current security compares with the required level of security. 

3. Implementation: establishing appropriate controls and policies to meet the requirements. 

4. Monitoring: continuous monitoring and recording of all activity within your systems. 

5. Audit: independent verification of compliance with internal and external audit programs. 

6. Improvement: adjusting the organization’s security based on audit findings. 

Controls, Audits, and Reporting 

Controls are the foundation of compliance; they can be either technical (e.g., security devices such as firewalls or encryption) or administrative (e.g., access policies and employee training). 

Audits are a method of determining if an organization’s controls are working effectively. Organizations must maintain sufficient documentation, logs, and evidence to demonstrate compliance with the requirements. 

Reporting is becoming increasingly important in the regulatory world as the timelines for incident notification are shortened. The failure to provide appropriate notice of a breach may result in severe consequences for the organization. 

Common Compliance Issues 

Even with established frameworks, companies still struggle to comply. Here are some reasons why: 

  • Complicated – There are many overlapping regulations. 
  • Cost – Investments in people and technology are needed. 
  • Large Organizations – There needs to be a way to manage compliance across large infrastructures. 
  • Human Error – People may not know how to comply; therefore, it is important to provide training. 

Companies can use technology, strategies, and customer commitment to address these issues. 

Best Practices for Enterprise Compliance 

To deal with the changing compliance landscape, enterprises would do well to follow these strategies: 

1. Align with Established Frameworks 

Companies should use a well-defined framework,, such as the NIST Cybersecurity Framework (NIST CSF), to establish a structured, accepted approach. 

2. Automate 

Automation tools can help reduce manual effort by enabling monitoring systems to detect anomalies and generate compliance reports. 

3. Regular Internal Audits 

Companies need to conduct internal audits regularly to identify gaps before external audits. 

4. Train Employees 

Most breaches result from human error. Having a well-developed training plan for all employees is critical to maintaining compliance. 

5. Integrate Compliance into Business Strategy 

Compliance should not be separate from the organization’s goals and risk management strategies. 

Consequences of Not Adhering to Cybersecurity Policy 

If you don’t comply with cybersecurity standards, then you could face: 

  • Economic penalties 
  • Legal consequences 
  • Loss of client confidence 
  • Business operations interruptions 

In certain circumstances, non-compliance can also restrict the company’s business operations, especially in regulated areas. 

Conclusion 

Due to the increasing number of regulatory requirements and the growing threat landscape, compliance must be a priority for US-based agencies to stay competitive and safe. NIST frameworks and CISA’s guidelines provide organizations with guidance for becoming compliant and secure through continuous implementation. 

Compliance with cybersecurity policy is now a critical part of daily business practices. Therefore, organizations committed to developing robust compliance processes will have the best chance of successful risk management, avoiding financial consequences, and remaining resilient throughout their lifecycles.

Source: Featured Articles 

In April 2026, a major intellectual property filing changed the digital landscape by focusing on the heart of modern computing. As American organizations try to manage the high energy demands of generative models while meeting sustainability goals, Microsoft’s new advances in in-chip microfluidics and optical communication provide a clear path forward. These changes show that the race to build bigger data centers is shifting toward denser, more efficient designs. As a result, Microsoft’s AI patent is moving the industry away from traditional air-cooled racks and roofs and toward high-density, vertically integrated compute modules.  

The Microfluid Breakthrough: Cooling the Silicon Core 

In 2026, the main challenge for US enterprises is not getting enough chips, but dealing with the heat they produce. Microsoft’s new patents describe a microfluidic cooling system that carves cooling channels directly into the back of the silicon chip. This lets liquid coolant flow precisely over the hottest parts of the GPU or TPU, bypassing traditional cold plates. This design can remove heat up to three times more efficiently than older methods.  

Moving to in-chip cooling means server racks can be much denser in existing buildings. US companies can now fit 60% more computing power into the same space without building new facilities. For organizations with limited space or power, this higher density is essential. It turns the data center from a large, spread-out site into a high-performance intelligence factory that uses electricity more efficiently.  

Optical Fabric: Breaking The Latency Barrier 

Besides cooling, Microsoft’s AI patent also tackles the networking slowdowns that affect large-scale model training. The patent describes a wide, slow optical setup that replaces copper connections with micro-LED-based light signals. This optical network lets data move between GPUs and shared memory almost as fast as light while using much less energy. For the large models of 2026, this change reduces communication overhead, which can account for up to 30% of training time.  

Switching to optical communication enables Microsoft to create a disaggregated data center where compute and memory are not tied to a single motherboard. In this setup, resources can be shared and directed as needed, much like air traffic control. This flexibility means expensive GPUs are not left waiting for data, which greatly improves the return on investment for infrastructure. Companies can expand their computing power without spending much more on networking hardware.  

Sustainable AI and Community Power Impacts 

The patents’ impact extends beyond the lab, affecting US power grids and communities. In early 2026, several states saw public concern over higher electricity bills caused by large data center growth. Microsoft’s move to sustainable light-based computing directly addresses these issues by lowering the energy needed for cooling and communication. These patents help make net-zero AI operations possible and better suited to local power limits.  

  • PUE efficiency: microfluidic cooling can drive power usage effectiveness (PUE) ratings down toward 1.05  
  • Water conservation: closed-loop liquid systems significantly reduce the millions of gallons of water typically evaporated in cooling towers  
  • Grid stability: dynamic workload routing prevents sudden power spikes that can destabilize local community grids  
  • Hardware longevity: precise thermal management reduces the mechanical stress on chips, extending the lifespan of expensive silicon assets  

The Rise Of Modular Super Factories 

These patents point to a larger shift toward modular global AI systems rather than single, massive sites. Microsoft Azure CTO, Mark Russinovich, says 2026 is the year of connected super factories that concentrate power across distributed networks. The patents outline how to build these factories so they can work in many settings, including locations near cities. This edge-to-cloud setup ensures fast AI services are available right where data is generated.  

Microsoft’s AI patent is especially important for the hybrid deployment models that US companies prefer. By using modular compute units with shared data Scratchpad memory, businesses can keep control over their data locally while still using global optical networks. This balance is crucial for industries such as finance and defense, where data must remain within specific areas. The patent helps make high-performance infrastructure more flexible and accessible for different needs.  

Preparing for the Post-GPU Era 

By the end of 2026, the focus is moving from just buying more GPUs to building system intelligence with specialized hardware. Microsoft is adding light-based chips and robotic systems to help maintain these very dense racks. These self-maintaining systems are the goal of this infrastructure change: platforms that run with little human help and high efficiency. This progress makes sure the next big jump in AI is both possible and sustainable.  

In summary, Microsoft’s latest patents mark a major change in US technology. Moving to microfluidic cooling and optical connections addresses the big problems of heat and energy that could have slowed AI progress. By fitting more computing power into smaller, more efficient spaces, Microsoft is making infrastructure faster, more reliable, and more sustainable for US businesses. The key takeaway is that the future of AI depends not just on software but on rethinking the physical systems that underpin it. Those who can best use these dense intelligence factories will have the edge.

Source: AI chips are getting hotter. A microfluidics breakthrough goes straight to the silicon to cool up to three times better. 

CERAWeek, often called the Davos of energy, brings together policymakers, producers, technologists, and financiers to discuss the future of global energy.  

At the conference last week, NVIDIA and Emerald AI introduced a new approach: treating AI factories as flexible, intelligent datasets instead of static power loads. Their collaboration combines accelerated computing, AI factory reference architectures, and real-time energy orchestration. This helps large AI deployments connect to the workload more quickly, operate more efficiently, and improve system reliability.  

This approach uses the NVIDIA Vera Rubin DSX AI factory reference design and Emerald AI’s Conductor platform to combine computing, networking, and control into a single system. The result is an AI factory that generates high-value AI tokens and can adjust to grid conditions as needed. This flexibility supports reliability and reduces the need to build extra infrastructure for peak demand.  

AES Constellation Energy, NextEra Energy, Nscale Energy and Power, and Vistra are working to increase energy generation capacity to meet rising demand. These companies plan to collaborate on strategies to support AI factories using the Nvidia and Emerald AI architecture. Their projects include hybrid setups with co-located power to speed up access to energy and benefit the wider grid by combining large AI loads with flexible operations, new resources, and smart controls. This approach makes the grid more reliable.  

This marks an important step for grid resilience backed by a network supporting AI factories. NVIDIA founder and CEO Jensen Huang describes this new computing infrastructure as a five-layer AI cake with energy as the base layer.  

Driving Improvements In Tokens Per Second Per Watt 

Power limits are changing how AI data centers operate. Now, energy efficiency, measured as tokens per second per watt, is the key metric for modern computing. By focusing on computational efficiency, organizations can cut costs, boost revenue, and build a stronger digital infrastructure for businesses and consumers everywhere.  

Power is a concern, but it’s not the only concern, Huang said on a recent Lex Fridman podcast. That’s why we’re pushing so hard on extreme code sign: to improve those tokens-per-second-per-watt orders of magnitude every single year.  

NVIDIA has consistently improved performance and energy efficiency since the NVIDIA Kepler GPU in 2012, up to the NVIDIA Vera Rubin platform this year. The number of tokens produced with the same power has grown by over a million times.  

Achieving this progress requires industry collaboration across all five layers of the AI stack, from energy and chips to infrastructure, models, and applications.  

Robotics, Digital Twins, and AI Upscaling Drive Energy Advances. 

At the event, NVIDIA ecosystem partners demonstrated how AI simulation and workforce innovation are accelerating the development of energy infrastructure for the intelligence era. Announcements from Maximum TerraPower and Adaptive Construction Solutions highlighted how AI is shortening timelines in construction, power generation, and workforce training.  

Maximo, a solar robotics company spun out of AES, announced it has completed a 100-megawatt robotic solar installation at AES’s Belfield site using AI-powered robotics built with NVIDIA accelerated computing, NVIDIA Omniverse batteries, and the NVIDIA Isaac Sim framework. Maximo demonstrated that autonomous installations can now operate reliably at a large scale. This method speeds up installation, improves safety and consistency, and helps meet the growing demand for electricity.  

TerraPower, in partnership with SoftServe, introduced a digital twin platform powered by NVIDIA Omniverse. This platform is designed to significantly reduce the time required to plan and design advanced nuclear plants by leveraging AI and simulation in early engineering. It cuts design cycles from years to months, speeds up the rollout of TerraPower’s Natrium energy plants, and improves both design and grid integration.  

Adaptive Construction Solutions, working with NVIDIA, announced a national apprenticeship program to help the skilled workers needed for AI factories and energy infrastructure. The program will expand training for key trades, open up more high-demand career opportunities, and support the fast growth of AI-powered energy systems.  

These efforts show how AI, digital twins, and workforce innovation are coming together to create faster, more reliable energy infrastructure.  

Working Together to Scale AI Factories for Reliable Power Grids 

GE Vernova, Schneider Electric, and Vertiv explained that digital twins, proven reference designs, and unified infrastructure are now key to scaling AI factories to reliably support the power grid. Their announcements focus on solving the power-to-rack challenge by designing AI systems as integrated energy and computing solutions from the start.  

GE Vernova described how detailed digital twins used with the NVIDIA Omniverse DSX Blueprint let utilities and developers simulate grid behavior, substations, and AI factory loads before anything is built. This kind of modeling helps test connection strategies, lower risks, and speed up getting power online in tight grid situations.  

Schneider Electric introduced new approved NVIDIA Vera Rubin reference designs and digital twins systems created with AVEVA. By simulating power cooling and controls in Omniverse, Schneider helps operators get the most out of every watt, check designs before building, and run AI factories more efficiently and reliably as they grow.  

Vertiv shared its approach to building physical infrastructure that is ready for simulation and based on reputable power and cooling modules. When combined with the Vera Rubin DSX reference design, this method simplifies design and deployment, helping AI factories scale up faster and with greater confidence.  

Together, these industry efforts offer a clear digital path with proven designs and infrastructure that help turn AI factories into flexible, grid-aware resources for efficient power use worldwide.  

Find out how NVIDIA and its partners are using AI and high-performance computing to improve energy solutions. 

Source: Efficiency at Scale: NVIDIA, Energy Leaders Accelerating Power‑Flexible AI Factories to Fortify the Grid 

The recent changes to American Cybersecurity policy indicate a new direction for U.S. agencies: compliance is now an ongoing operational requirement, not a periodic one. New guidelines, advisories, and framework changes are pushing businesses to upgrade their cybersecurity preparedness, invest in infrastructure, and prepare for more rigorous audit requirements. 

Updates from CISA, NIST, and other organizations, such as the DOE, indicate that companies will face an increasing regulatory burden in the future. These regulatory changes are not occurring in isolation but are part of a much larger initiative to address the growing number of cyber threats targeting critical infrastructure and the private sector. 

Shift from Reactive to Proactive Compliance 

Prior to recent policy changes, cybersecurity compliance in the U.S. was largely reactive, often triggered by an incident or an audit. However, the shift towards more proactive risk management and the ongoing monitoring and reporting of security events is now emphasized under the updated guidelines. 

As part of the new expectations, companies must: 

  • Identify potential vulnerabilities before they are exploited 
  •  Have continuous threat detection in place 
  •  Maintain complete audit trails for all security monitoring and controls 

This approach to compliance will be more critical for industries such as financial services, energy, healthcare, and tech, where cyber exposures and risks can affect the national level. 

Impacted Companies Will Face Key Policy Changes 

1. Greater Requirements for Reporting 

There are new policies expanding the requirements for incident reporting. Organizations will now have to report breaches in shorter timeframes, usually within days rather than weeks. 

2. Adoption of Zero Trust Architecture 

Federal guidance is encouraging, if not requiring, the adoption of the Zero Trust principle. The assumption is that no user or system should, by default, be trusted at all, including those on the same network. 

3. Requirements for Supply Chain Security Measures 

Policies now emphasize third-party risk management. Vendors and partners are expected to meet stringent cybersecurity requirements, especially given the rising incidence of attacks across the supply chain. 

4. Protection of Critical Infrastructure 

The Department of Energy and other agencies are focusing on the strategic security of energy grids and industrial control systems, given their vulnerability to cyberattacks. 

Challenges to Implementation 

While these policy updates are intended to strengthen security, they will each present their own unique challenges: 

  • Infrastructure upgrades: Legacy systems may not be able to support modern security frameworks 
  • Cost increases: Due to the expanding employer base and the costs of tools, personnel, and training 
  • Talent shortages: Demand for cybersecurity professionals is exceeding the available supply 

Companies need to balance compliance with efficient operations and ensure that their security procedures do not disrupt the business’s ability to operate normally. 

The Workflow of Policies Impacting Business 

The figure below visualizes the significant flow of new cybersecurity policies through business. 

Announce Policy → Assess Risk → Upgrade Infrastructure → Implement Compliance → Continuously Monitor → Audit/Reports 

The image above illustrates how compliance is an ongoing process. A traditional view would have a business reach completion; however, a business continues to adjust as policies evolve and as new threats occur. 

Impact of Updates to NIST Framework 

The NIST Cybersecurity Framework is foundational to achieving enterprise compliance. Recent updates include: 

  • Integration of AI and automation into security operations 
  • Improved guidance for managing supply chain risk 
  • Greater focus on identity and access management 

This update aligns closely with the principles of Zero Trust; specifically, the importance of robust identity verification and access control. 

Sector-Specific Repercussions 

Energy Sector 

Department of Energy guidance promotes greater protection against threats to the power grid and operational technology systems. 

Financial Sector 

Regulators have increased scrutiny over financial institutions; faster reporting of data breaches and increased protection of customer data will become key metrics in the regulatory examination process. 

Technology Sector 

Technology vendors are now required to demonstrate compliance with evolving security standards when providing their products or services to government entities. 

Costs Associated with Compliance and Strategic Planning 

As a result of these policy changes, the financial impact will be significant. Companies are spending more money on cybersecurity than they have ever spent before due to: 

• Required Regulation 

• Increased premiums for Cyber Insurance 

• Possible fines for not being in compliance 

However, organizations that invest strategically can turn their compliance into a competitive edge by demonstrating to customers and partners that they are trustworthy. 

Importance of That in the United States 

Cybersecurity has become a national priority. Companies need to play an important role in maintaining the nation’s overall digital resiliency. Companies that fail to comply with changes in the law may face legal liability, operational disruptions, and reputational damage. 

Conversely, companies that take a proactive approach to compliance and strengthen their cybersecurity posture will experience reduced risk, improved long-term sustainability, and greater overall business viability. 

Source: Cybersecurity Directives 

In April 2026, targeted digital attacks against American industrial and corporate centers have sharply increased. On April 14, CISA, the FBI, and the NSA issued a joint advisory warning of a widespread crisis involving Internet-exposed programmable logic controllers (PLCs) and endpoint management software. The new federal guidance makes it clear that attackers are now actively disrupting operational technology (OT) in the energy, water, and manufacturing sectors, not just gathering information. CISA is calling for urgent action from US enterprises to secure the vital connections between digital networks and physical infrastructure.  

Securing the Industrial Edge: The PLC Crisis 

The April 2026 advisory’s top concern is that many PLCs are exposed to the public internet. Iranian-linked attackers have been seen changing project files and data in these controllers, causing real-world disruptions. Since these small computers control critical systems such as utilities and pumps, keeping them secure is essential to public safety. CISA is urging operators to quickly check their external-facing ports and disconnect any controllers from direct internet access.  

The advisory also calls for strong gateway security when remote access is needed. Organizations should put industrial systems behind VPNs or bastion hosts that require phishing-resistant multi-factor authentication (MFA). Older protocols such as Modbus and BACnet, which typically lack built-in encryption, should be run over secure tunnels to prevent unauthorized changes. This kind of isolation is the main defense against the attacks now affecting the US grid.  

Hardening Endpoint Management After Major Breaches 

After a major device wiping attack on Stryker Corp in March 2026, CISA is now focusing on securing endpoint management systems. Attackers have been using legitimate tools such as Microsoft Intune to issue unauthorized commands across company devices. The April advisory tells US businesses to use multi-admin approval for sensitive actions, such as device wiping or running scripts that require a second set of credentials for risky changes, to help prevent damage if one admin account is compromised.  

The CISA advisory also highlights the need for better privileged identity management (PIM) to stop attackers from moving through networks. Organizations should move to just-in-time (JIT) access, giving admin rights only for specific tasks and only as long as needed. This reduces the risk by removing permanent admin accounts, which are a common target for attackers. Careful log monitoring for strange API activity also helps prevent management software from being used as a remote access Trojan (RAT).  

Remediating the Known Exploited Vulnerabilities (KEV) Catalog 

In April 2026, CISA added several new entries to its Known Exploited Vulnerabilities (KEV) catalog, including major flaws in Fortinet, Microsoft, and Adobe products. One key issue is CVE-2026-21643, a serious SQL injection vulnerability in FortiClient EMS that allows attackers to run code remotely without logging in. Federal agencies and private partners had to fix these by April 16, 2026, because they were likely to be exploited right away. Focusing on the KEV list helps security teams with limited resources address the most urgent threats.  

The Convergence Of IT And OT Security 

As industrial sites rely on more data, the distinction between business networks and production systems has blurred. The April advisory warns that attackers often use compromised office computers to gain access to OT management systems. To address this, companies are using unified security platforms that consolidate IT and OT data in a single place. Spotting anomalies like a forged BACnet request or an unusual Modbus write requires a strong understanding of industrial protocols, which many standard IT tools lack.  

Implementing Post-Quantum Readiness 

Another important part of the 2026 advisory is the push for crypto agility amid growing threats from quantum computing. CISA is asking critical infrastructure sectors to start listing their cryptographic assets to prepare for post-quantum cryptography (PQC), even though the risk of harvesting now to decrypt later is a long-term issue. Updating old industrial systems will take a lot of work. Starting now helps ensure that long-term equipment, such as power grid controllers, remains secure for years to come. Vulnerability scans are officially over, replaced by continuous exposure management (CEM). CISA’s latest guidance encourages a shift toward attack-surface management tools that provide real-time visibility into every asset, from cloud buckets to edge gardening kits. By continually testing defenses against simulated AI-driven attacks, US enterprises can identify weak links before adversaries do. This proactive mentality is the only way to sustain resilience in a landscape where the time to exploit has shrunk to minutes.  

The CISA advisory signals urgent fixes for US enterprises to move away from static security checklists toward a more dynamic intent-based defense model. Boards of directors are increasingly held liable for these systemic failures, making cybersecurity a central pillar of corporate governance. By aligning with federal mitigation strategies, American businesses can protect their intellectual property and ensure the continuity of essential services. The April 2026 reset is a clear signal that the cost of inaction has finally surpassed the cost of comprehensive defense.  

To sum up, the federal warnings from April 2026 mark a major shift in US digital security. The focus is now on fixing exposed industrial hardware and strengthening management software right away. US companies that keep track of their assets, use multi-admin approval, and remove default credentials will be better prepared for fast-moving threats. In the end, national resilience relies on both private and public sectors, treating cybersecurity as essential. Ignoring these urgent fixes risks not only data loss, but also large-scale physical and financial harm.

Source: Read and watch the latest news, multimedia, and other important communications from CISA. 

With the fast-paced rise in AI usage throughout all sectors, compliance is beginning to represent one of an organization’s greatest and most complex costs due to changes in the regulatory environment between the US and EU, increasing the cost of operations for organizations, which ups the stakes of how and where to deploy AI systems. 

Various forward-thinking frameworks have been created by the SEC, the European Commission & the National Institute of Standards & Technology (NIST), providing evidence that the global compliance landscape is very fragmented. The compliance challenge is not solely a legal one for businesses; it is also a financial one. 

The Fundamental Difference: Principles vs Regulation 

The methods used by the EU & US are vastly different when it comes to AI governance. 

In the US, AI is governed under a principles-based approach. The key points of this approach are risk management, transparency, and voluntary compliance. The NIST AI Risk Management Framework is an example of this, as it provides companies with guidelines without imposing strict legal consequences. 

On the other hand, the EU has taken a rules-based approach to AI through the AI Act, which establishes rules for AI systems based on the risk level assigned to them and thus mandates compliance for systems according to their risk level. Businesses that utilize high-risk systems must adhere to strict guidelines requiring them to create documentation for the system, ensure human oversight, and perform conformity assessments to validate that the system has been properly developed. 

Three Factors Driving Up AI Compliance Costs 

There are three key drivers causing AI compliance expenses to rise: 

  • Compliance challenges due to the increasing length and complexity of regulatory requirements. Compliance teams will be responsible for interpreting and implementing several frameworks across multiple jurisdictions. As a result, they will require both legal support and ongoing case management. 
  • Document and audit requirements related to regulations requiring infrastructure funding, due to the extensive documentation (i.e., training data documentation, algorithm explainability, & risk assessments), must be created on behalf of users. Thus, additional personnel will be required to perform these functions. 
  • The stringent compliance processes that typically slow product launches can negatively impact time-to-market and erode competitive advantage. 
Factor United States European Union 
Regulatory Approach Principles-based Rules-based (AI Act) 
Compliance Cost Moderate High 
Documentation Flexible Extensive 
Penalties Limited Significant fines 
Deployment Speed Faster Slower due to checks 

The Hidden Costs of AI Regulation 

While there are direct costs to comply with AI regulations, indirect costs can have an even greater impact on organizations: 

  • Operational delays in deploying AI solutions will hinder revenue generation. 
  • Increased demand for legal and compliance professionals, driven by demand for legal compliance and legal experts, will raise costs. 
  • Due to the increased workload of compliance professionals, systems may need to be restructured to meet EU-compliant standards. 

Take, for example, an AI-driven recruitment tool; this would likely require additional bias audits and natural language processing (NLP) capabilities to comply with European regulations, resulting in increased time and expense for that type of development, as well as associated costs. 

Strategic Measures Taken By Corporations 

To address the rising costs of regulatory compliance, firms are using a variety of techniques/strategies. 

1. Regionally Specific/Regional Deployment Models. For example, there are various versions of AI available in the marketplace, such as a minimal-restriction version that may be available or deployed in the USA, compared to fully compliant versions built for the EU. 

2. Investing in Compliance Infrastructure. Organizations are developing their in-house Compliance departments and implementing automated solutions to ensure there’s active monitoring of AI products and applications. 

3. Aligning Corporate Strategy WITH Global Standards. Many organizations are also aligning their company’s compliance strategies with frameworks such as NIST, providing a benchmark they can use to comply with new, stricter regulations when they become enforceable. 

The Role of Risk Management Frameworks 

The NIST AI Risk Management framework plays an essential role in helping U.S. companies prepare for upcoming regulatory changes. The NIST AI Risk Management Framework is designed to help companies manage their compliance and adopt a structured approach. 

  • Governance & Accountability 
  • Data Quality & Data Integrity 
  • Continuous Monitoring of AI Products. 

Although the NIST AI Risk Management Framework is not a legally binding document, it is foundational for organizations seeking to become compliant and prepared for regulatory changes. 

Long-Term Implications 

The long-term effects of the United States and European Union’s differing positions on artificial intelligence policy will have a significant impact on the global economy. For example, the high cost of compliance with regulations could limit the ability of SMEs (small-to-medium enterprises) to invest in new ideas and products; companies will be incentivized to move their resources to regions with less strict regulatory requirements; and eventually, a global standard will develop to reduce the complexity associated with maintaining compliance. 

The advent of the global AI economy presents businesses in the United States with an opportunity to develop new revenue streams through international partnerships and to create globally compliant products. However, given that many businesses in the United States have no option but to comply with EU regulations regardless of where they operate, non-compliance carries the risk of heavy fines, legal action, and damage to credibility in the international market. 

Why This Matters in the US 

For US businesses, compliance is no longer optional. Even if operations are domestic, global partnerships and data flows often bring EU regulations into scope. Failure to comply can result in fines, legal action, and reputational damage. 

At the same time, over-investing in compliance without strategic planning can reduce profitability. The challenge lies in balancing innovation with regulation ensuring that AI systems remain both competitive and compliant. 

Source: Latest Press Releases 

The Cybersecurity and Infrastructure Security Agency’s latest threat advisories have further established an unfortunate reality, Cybersecurity is no longer simply a reactive function; it is now treated as an enterprise-wide strategic decision. Choosing the wrong cybersecurity platform increases the risk of a breach on that platform; it can also lead to significant financial losses, damage to your company’s reputation, and even fines for regulatory violations. 

Central to the enterprise-wide decision-making process is a difficult comparison: EDR (Endpoint Detection and Response) vs. XDR (Extended Detection and Response). Both EDR and XDR provide organizations with the tools to detect and respond to cyber threats; however, they differ significantly in scope, scalability, and operational impact. 

Understanding EDR vs. XDR 

EDR solutions focus on monitoring endpoints, i.e., computers, laptops, servers, and mobile endpoints. EDRs allow enterprises to monitor endpoint activity, identify anomalous activities, and help incident response teams to quickly isolate the threat. However, most modern cyberattacks involve multiple components and connections, so EDR alone is not sufficient to stop them. 

The XDR model consolidates visibility across multiple security layers (i.e., endpoints, networks, cloud workloads, and email) to correlate data across all sources and improve the ability to quickly detect cyber threats. As confirmed by CrowdStrike and Microsoft, the use of XDR reduces alert fatigue by centralizing security data and speeding incident response. 

The Rise and Rise of CISA Alerts Stimulating Upgrades to XDRs 

Recent alerts have illustrated the complexity of emerging threats, from ransomware to supply chain attacks and zero-day vulnerabilities. They exploit the gaps between various security solutions. That gap is also where XDR (extended detection and response) excels. 

Companies that rely primarily on EDR, or endpoint detection and response, typically face the following challenges: 

  •  Limited visibility into the disparate elements of their security solution(s) 
  •  Delayed correlation of identified threats 
  •  Difficult-to-manage manual incident response workflows 

In contrast, XDR enables endpoint threats to be automatically correlated and responded to, thereby significantly diminishing dwell time the amount of time an attacker remains undetected in a targeted environment. 

Feature EDR XDR 
Scope Endpoint-only Multi-layer (endpoint, network, cloud) 
Detection Behavior-based Correlated multi-source detection 
Response Manual/limited automation Automated, orchestrated response 
Visibility Partial Unified 
Cost Lower initial Higher but scalable ROI 

Detection, prevention, and automated response 

Modern cybersecurity solutions ensure the full operation of the three essential functions for enterprise Cybersecurity: 

1. Detection 

EDR detects anomalies at the endpoint level, while XDR can detect anomalous behavior by correlating events across all systems and environments. Under the EDR heading, you would detect that a user received a phishing email; later, that same user had an unusual login; and later, was moving laterally throughout the environment. XDR would identify all those events as anomalous by correlating events across disparate systems. 

2. Prevention 

Prevention encompasses all applicable elements of proactive, AI-driven anomaly detection. With XDR, threat intelligence feeds into the solution will improve predictive capabilities across the enterprise. 

3. Automated Response 

Where XDR provides the most value is via automation. XDR can automatically isolate compromised end users/devices; block malicious IP addresses; and trigger alerts or notifications without manual intervention, all of which is critical to large enterprise networks with hundreds or thousands of endpoints. 

Cost vs Value – Balancing Compensation and Worth 

EDR products may have a lower upfront cost, but they will typically require other products for network/cloud protection. Therefore, they will add complexity and increase costs over time. Conversely, the initial costs of acquiring an XDR solution will be higher, but it will consolidate multiple products into a single product line, thereby reducing overhead and increasing efficiency. 

As the cost of cyberattacks is generally in the millions, more and more companies are justifying investment in an integrated platform. 

Selecting A Technology 

When determining whether to implement EDR or XDR, each type of organization should consider its level of maturity (as follows): 

  • Small and Medium-Sized Enterprises: EDR may be adequate based on limited business infrastructure. 
  • Larger corporations: XDR will be critical to giving a complete view of the organization. 
  • Organizations in Highly Regulated Areas: XDR will give organizations the best opportunity to comply with governmental regulations and be prepared for audits. 

The Evolution of Cybersecurity Services for Enterprises 

The industry is undergoing a trend toward integration and the development of artificial intelligence-based defensive capabilities. A growing number of vendors are also integrating machine learning into their products, enabling them to automatically learn and adapt to new attack methods. As more and more employees use the cloud and work off-premises, the XDR product will become the standard. 

Source: Read and watch the latest news, multimedia, and other important 

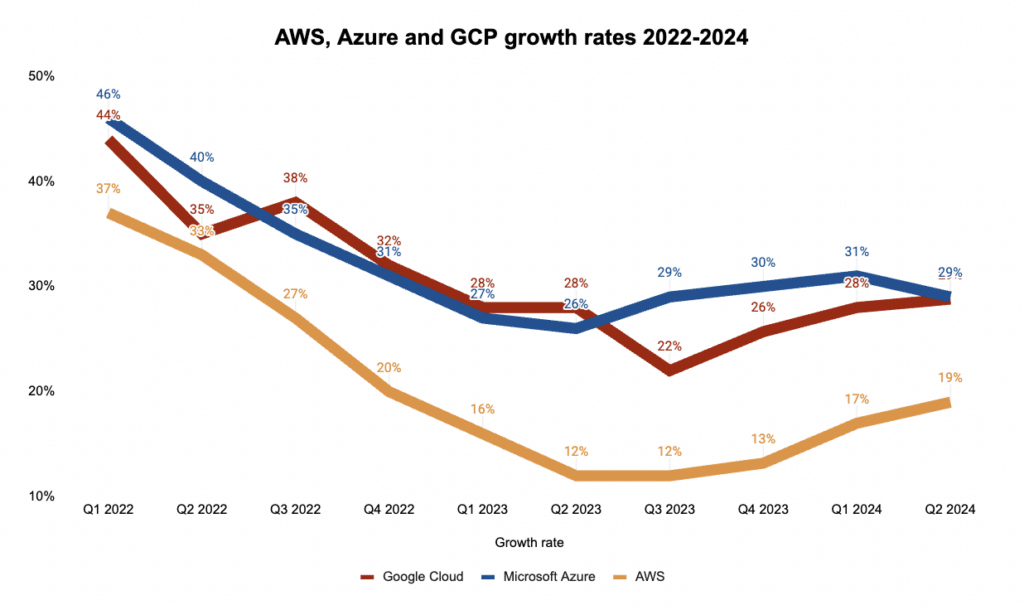
As artificial intelligence rapidly advances in 2026, American companies are rethinking their infrastructure strategies. Many are shifting from general cloud storage to specialized intelligence factories, leading to a key decision between the two top infrastructure providers. One offers a wide modular selection of models, while the other focuses on a tightly integrated system built for large-scale data processing. This analysis looks at the main differences in performance, flexibility, and cost as organizations adapt to these changes.  

Architectural Philosophies: Breadth Versus Integration 

In 2026, Amazon Web Services (AWS) stands out for its modern, agnostic approach with its Bedrock platform. Instead of limiting users to a single model family, AWS lets developers switch between Anthropic’s Claude, Meta’s Llama, and its own Titan models via a single API. This flexibility helps US companies avoid vendor lock-in and adapt quickly as models change. By making AI modular, AWS gives teams the freedom to pick the best fit for each business need.  

Google Cloud Platform (GCP) has taken a different path by focusing on vertical integration with its Vertex AI platform and Gemini model family. Its main strength is the unified data foundation, which connects machine learning models directly to BigQuery and Looker, removing the need for complicated data pipelines. This setup lets data scientists train and deploy models directly on live data, saving time on data preparation for industries like retail and healthcare that handle large volumes of data. This zero-copy design offers speed that modular systems often cannot match.  

Computing Performance and Custom Silicon 

When comparing Google Cloud and AWS for AI, much of the focus is on their specialized chips that help lower insurance costs. AWS has expanded its Trainium and Inferentia chips, offering a 40-50% cost-performance boost over standard GPU instances for long-term production workloads. These chips work well with the Neuron SDK, which supports popular frameworks like PyTorch and TensorFlow. For startups growing quickly, these custom chips are key to keeping costs down as their computing needs rise.  

Google leads in custom acceleration with its seventh-generation Tensor Processing Units (TPUs) called V7 Ironwood in 2026. These are the same chips that power Google Search and YouTube, delivering top performance for training the largest multimodal models. Unlike AWS’s more general-purpose chips, TPUs are designed for JAX and XLA, making them ideal for teams working on very large models. For organizations planning to train trillion-parameter models from the ground up, TPU Pods remain the best in the industry.  

Developer Experience And MLOps Maturity 

The overall developer experience plays a big role in how US engineering teams choose their platforms. GCP is often called the engineer’s cloud because it offers an easy-to-use console and the strongest managed Kubernetes service (GKE). Vertex AI helps speed up the MLOps process with AutoML features that can cut model development time by almost sixty percent for common tasks like classification and regression. This focus on helping developers move quickly makes GCP a top choice for AI-focused startups that need to stay ahead of the competition.  

AWS’s SageMaker can be harder to use, but it is still the most complete machine learning platform for established businesses. It has strong governance and audit tools, which are important for industries like finance and defense. SageMaker’s Canvas lets business analysts work without code, while Studio gives advanced users detailed control over the training process. For large organizations with teams of varying skill levels, SageMaker’s wide range of features offers a thorough, though sometimes more challenging, path to production.  

Token Economics And Pricing Models 

By 2026, the financial side of Google Cloud versus AWS AI will depend more on token economics than on hourly rates. AWS Bedrock uses a serverless pricing model, where you pay only for each request, making it a good fit for businesses with unpredictable or sudden traffic spikes. This approach eliminates the extra costs associated with unused resources in older systems. Also, AWS offers tiered pricing for long-term use, which can reduce inference costs by up to 65% for companies with steady, high-volume workloads.  

Google Cloud offers a special sustained use discount that automatically lowers rates as you use more resources during the month, with no upfront contract required. This is helpful for startups, letting them grow without worrying about sudden cost increases. Google also offers committed use discounts (CUDs) for TPUs, providing organizations with a stable cost for large, long-term training projects. By matching pricing to actual hardware use, Google ensures costs grow in line with the value you get.  

Conclusion 

Choosing between these two major platforms means weighing whether your organization needs flexible options or robust data integration. AWS is the top pick for companies that want the widest range of models and the best enterprise governance tools. It is designed for a hybrid environment, offering the stability and range needed to support both older systems and new technologies. For teams that want full control over their models, AWS stands out as the market leader.  

On the other hand, Google Cloud is the best choice for organizations that see data as their main advantage. Its fast networking, built-in data analytics, and top-tier TPU infrastructure make it a great place to build the next wave of AI applications. As demand for the system grows in the US through 2026, being able to turn raw data into useful insights easily will set companies apart. In the end, the real winner is the business that aligns its cloud setup with its long-term AI goals.

Source: AWS Bedrock vs Google Vertex AI vs Azure AI Studio: Enterprise AI Platform Comparison 2026