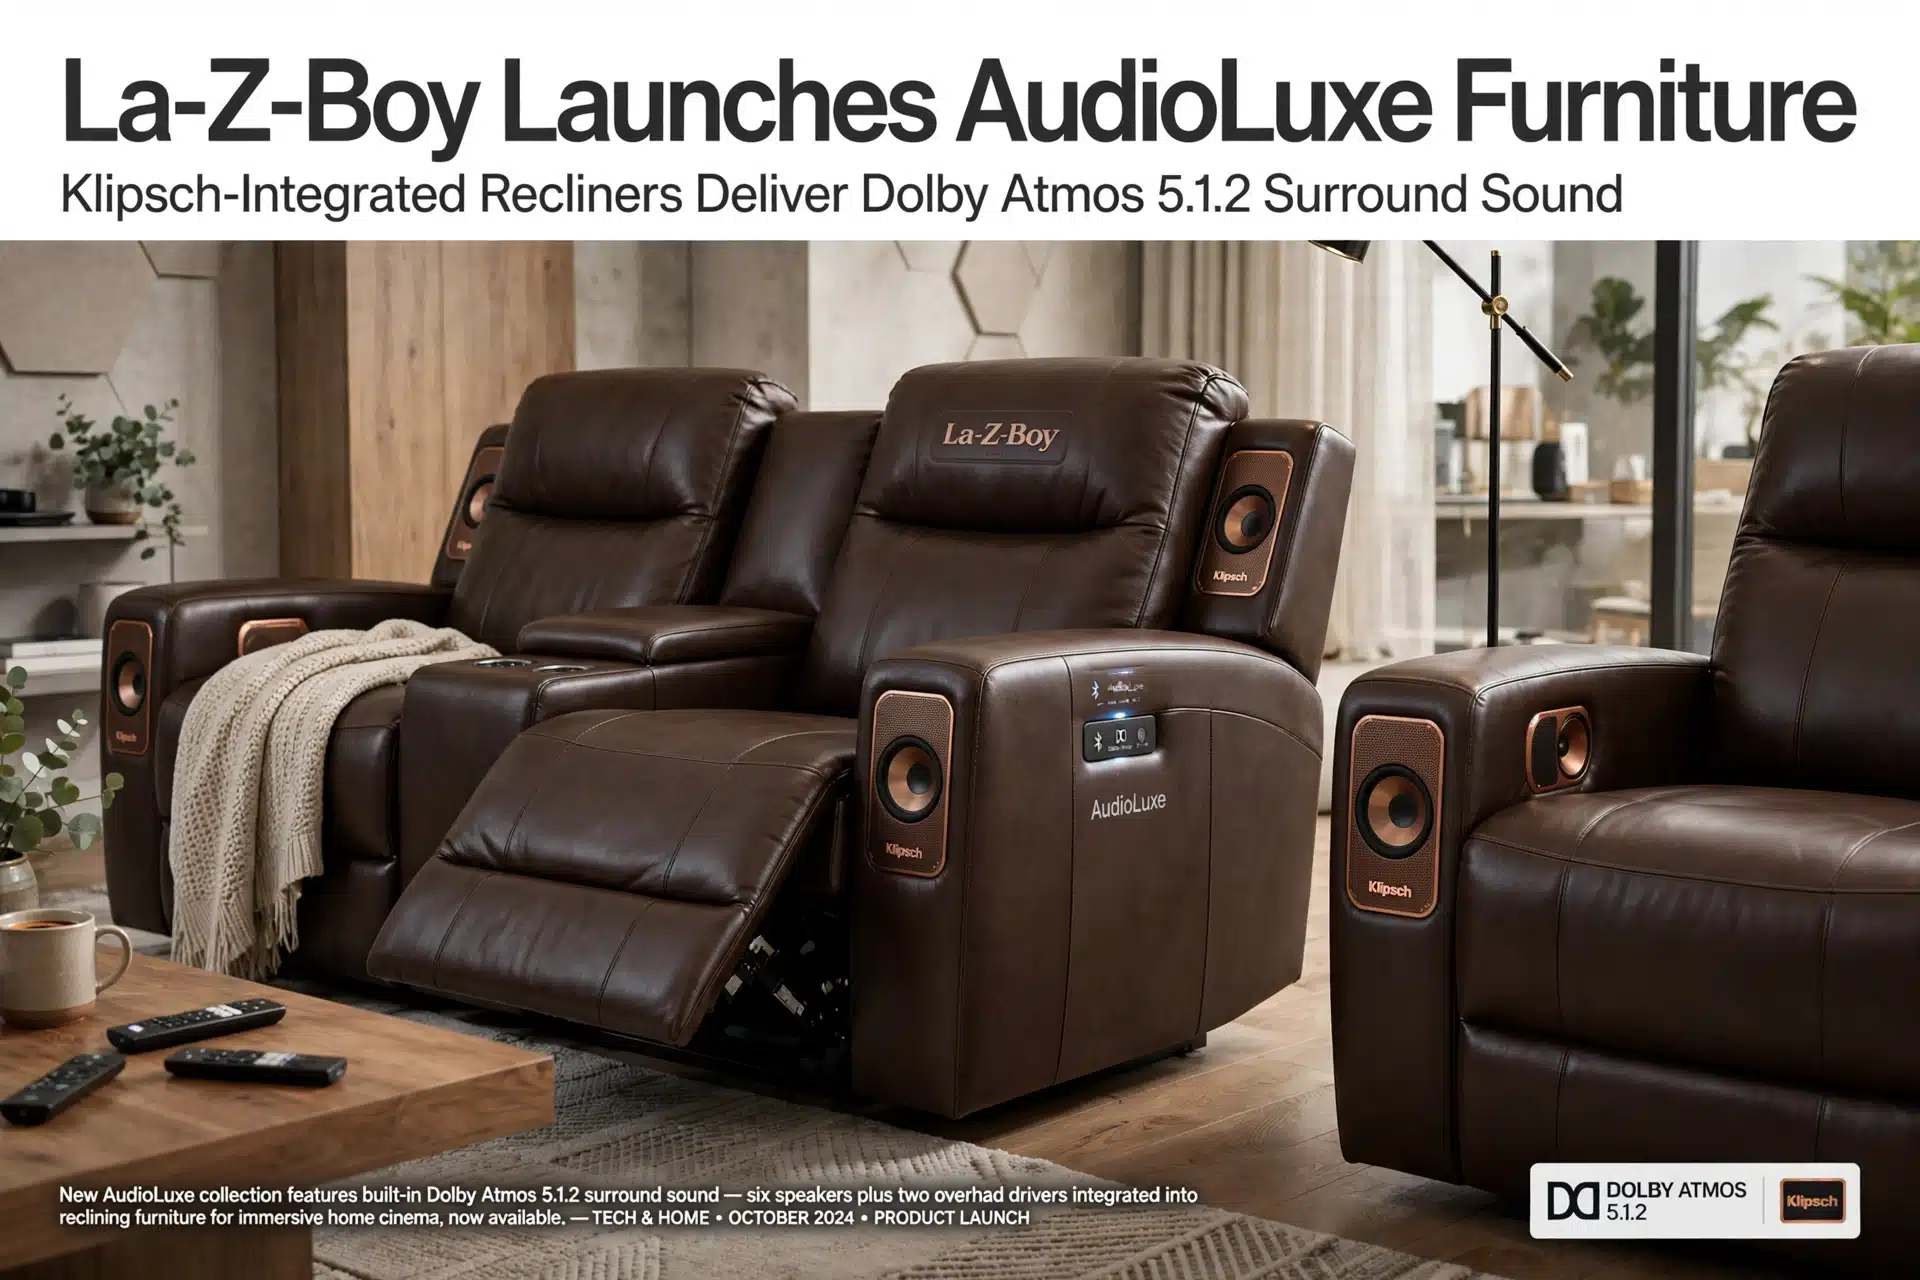
Blending traditional home comfort with high-performance consumer electronics, furniture manufacturer La-Z-Boy officially debuted its AudioLuxe product line in retail stores nationwide [cite: 2.2.4]. Featuring integrated ‘Sound by Klipsch’ technology, AudioLuxe embeds premium speakers and subwoofers directly into recliners and motion seating [cite: 2.2.4]. Announced on October 21, 2026, the launch represents a significant design evolution in smart home furnishings, offering US consumers an immersive acoustic experience without the visual clutter of standalone surround-sound speaker systems.

The Evolution of Smart Home Entertainment and Furniture

For decades, home audio enthusiasts faced a perennial design compromise: achieving high-fidelity sound required filling living rooms with bulky floor-standing speakers, tangled wiring, and wall-mounted acoustic panels. As living spaces become increasingly multi-functional, consumer electronics brands and furniture makers are collaborating to embed sophisticated technology directly into everyday household items.

La-Z-Boy’s collaboration with acoustic engineering pioneer Klipsch addresses this exact design challenge. By housing custom-tuned drivers, amplifiers, and subwoofers within the internal framework of plush motion recliners, AudioLuxe delivers tactile, directional sound directly to the listener. Users can stream audio wirelessly from televisions, smartphones, or gaming consoles while experiencing acoustic resonance transmitted physically through the chair structure.

Engineering Acoustic Comfort: Inside the AudioLuxe Build

Developing furniture with integrated audio requires rigorous acoustic isolation and vibration dampening. If speakers are mounted incorrectly inside a reclining mechanism, mechanical rattling and structural resonance can distort sound clarity. Klipsch engineers spent months tuning the driver placement and internal cabinet acoustics within La-Z-Boy’s proprietary frame architecture.

The resulting furniture line pairs signature zero-gravity reclining ergonomics, power headrests, and lumbar support with crystal-clear audio reproduction. Reviewers note that low-frequency subwoofers built into the base deliver tactile bass responses during movie viewings and gaming sessions, creating a multi-sensory immersion that traditional couch setups struggle to replicate.

Broader Consumer Tech Trends in Smart Home Seating

The launch of AudioLuxe arrives alongside a wave of consumer tech innovations aimed at transforming living spaces. From AI-powered guitar amplifiers [cite: 2.2.3] to ergonomic wellness recliners featuring advanced temperature control and massage articulation [cite: 2.2.4], manufacturers are leaning heavily into consumer insights that prioritize convenience, relaxation, and integrated entertainment.

Industry analysts observe that modern home buyers are increasingly willing to invest in premium, connected furnishings that serve dual purposes. By bridging the gap between high-end audio and ergonomic seating, La-Z-Boy’s latest collection exemplifies how legacy brands can modernize their product portfolios for tech-savvy households.

Pricing, Availability, and Store Rollout

AudioLuxe furniture is arriving in select La-Z-Boy retail showrooms across the United States [cite: 2.2.4], alongside expanded assortments of PowerLift recliners featuring zero-gravity functionality and high-performance iClean stain-resistant fabrics [cite: 2.2.4].

Pricing varies depending on upholstery customization and seating configuration, positioning AudioLuxe as a premium tier offering for consumers seeking luxury home theater integration.

Frequently Asked Questions

Q: What is La-Z-Boy AudioLuxe? AudioLuxe is La-Z-Boy’s new premium audio furniture line featuring integrated speakers and subwoofers powered by Klipsch acoustic technology [cite: 2.2.4].

Q: How does the integrated sound system work? It features custom-tuned drivers and subwoofers embedded directly into the recliner framework, allowing wireless audio streaming and tactile sound immersion [cite: 2.2.4].

Q: Where can consumers purchase AudioLuxe furniture? The new line is rolling out to select La-Z-Boy retail stores across the United States [cite: 2.2.4].

Conclusion

La-Z-Boy’s AudioLuxe launch demonstrates the successful marriage of acoustic engineering and ergonomic furniture design. By integrating Klipsch sound systems directly into recliners, the brand offers US consumers a sleek, clutter-free solution for immersive home entertainment.

Sources

Reference 1: • PR Newswire / La-Z-Boy Incorporated (October 21, 2026): ‘Consumer Insights Shape La‑Z‑Boy’s Latest Innovations, Including the New PowerLift Chair Collection and AudioLuxe’ – https://www.prnewswire.com/news-releases/consumer-insights-shape-la-z-boys-latest-innovations-including-the-new-powerlift-chair-collection-and-audioluxe-302915974.html [cite: 2.2.4]
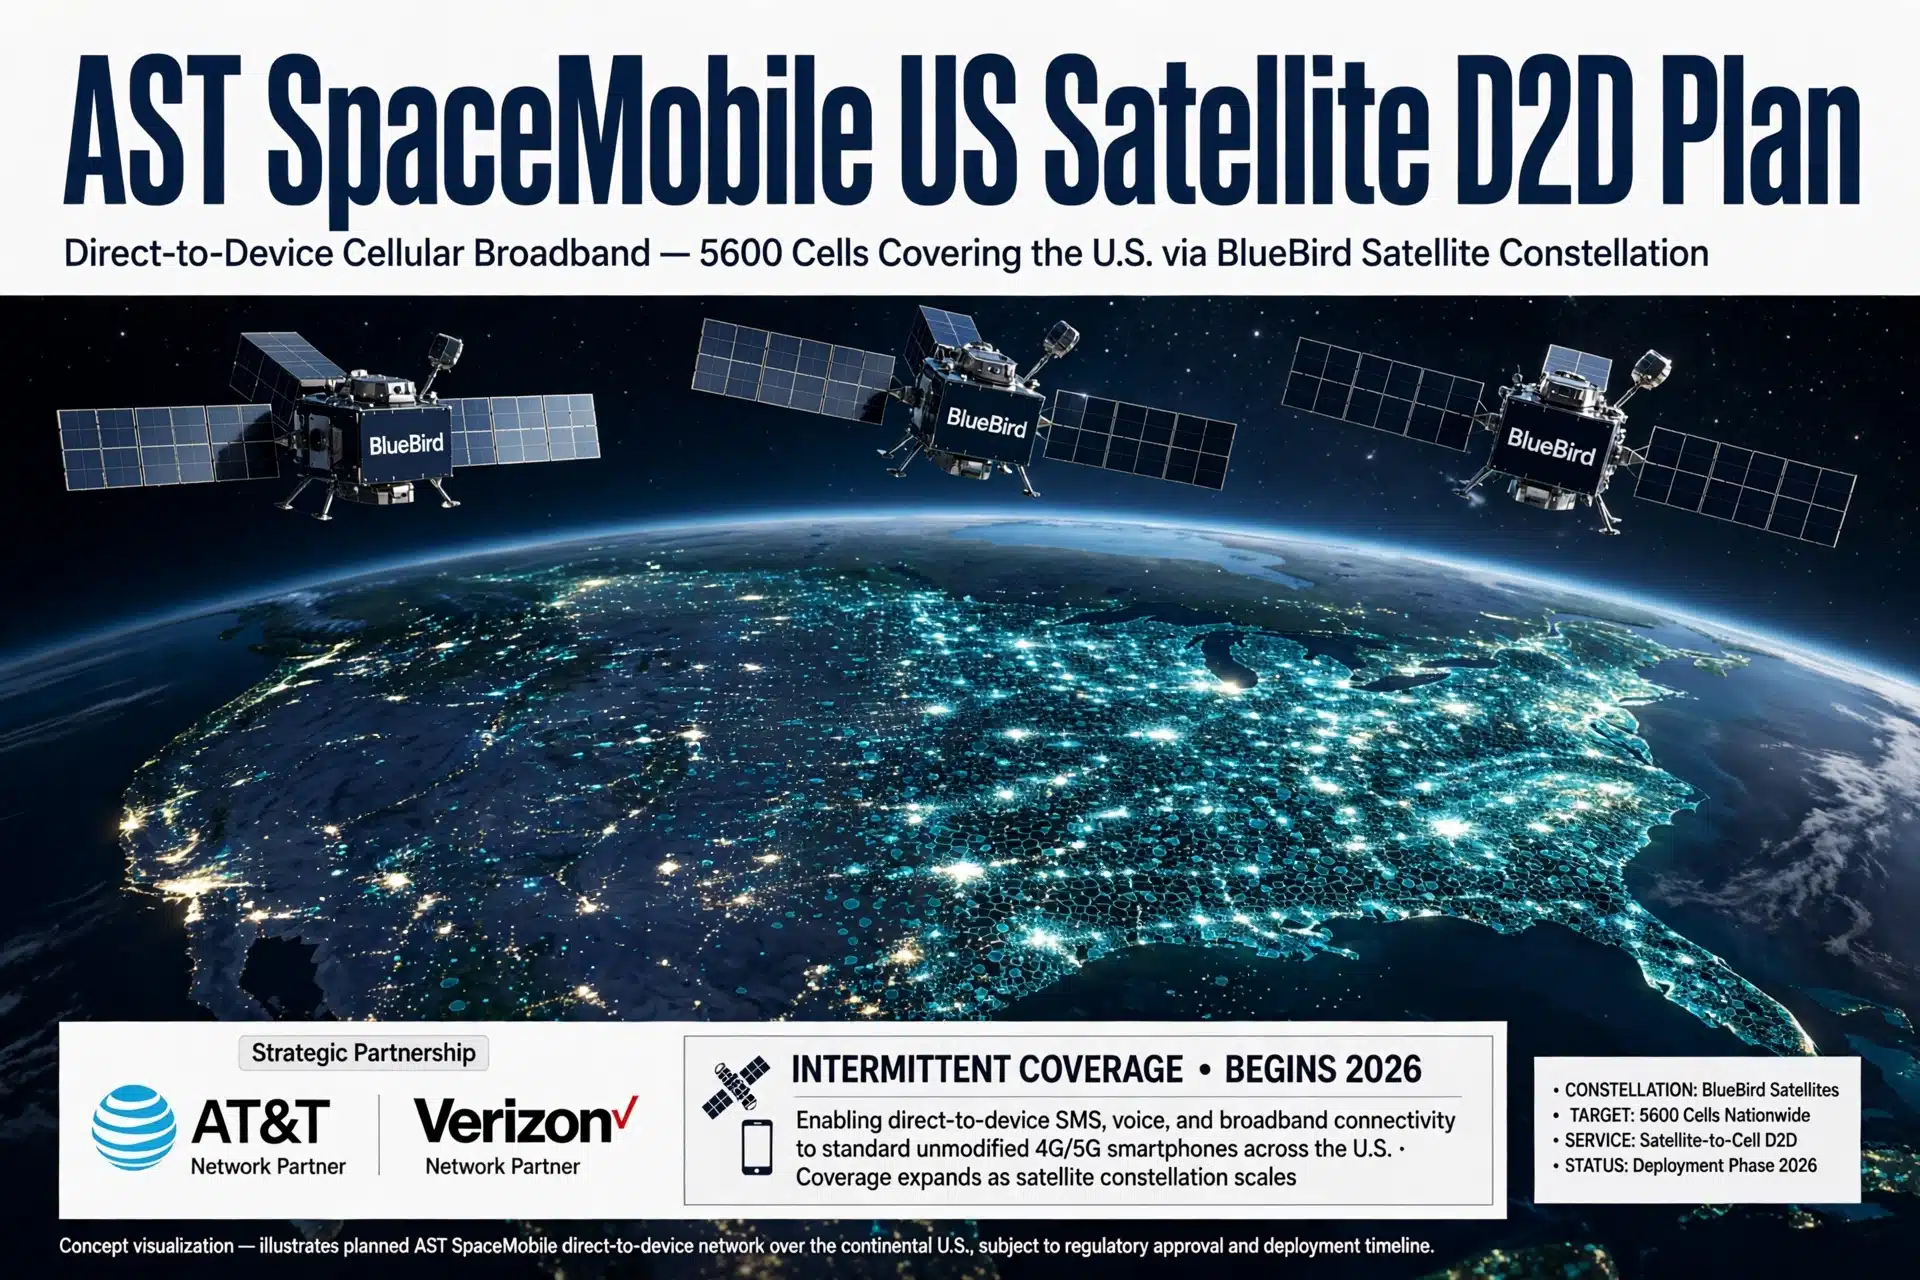
In an update impacting the future of mobile connectivity, satellite communications developer AST SpaceMobile announced on October 21, 2026, that it is targeting initial, intermittent direct-to-device (D2D) broadband coverage across the United States and international markets before the close of the year [cite: 2.1.5]. Designed to bridge dead zones and eliminate terrestrial cellular gaps, the company’s space-based cellular broadband network aims to connect unmodified, everyday smartphones directly to low-earth orbit (LEO) satellites without requiring specialized hardware.

The Technical Mechanics of Direct-to-Cell Satellite Broadband

Direct-to-device satellite communication represents one of the most ambitious engineering challenges in modern telecommunications. Traditional satellite phones require bulky, dedicated transceiver dishes and specialized antennas. In contrast, AST SpaceMobile’s architecture deploys massive phased-array antennas in low-earth orbit capable of communicating directly with standard cellular handsets operating on commercial frequencies.

Industry analysts following the rollout note that initial service will be characterized by intermittent connectivity windows as satellites pass overhead [cite: 2.1.5]. Because the current constellation size is still expanding toward full commercial density, users will experience coverage in targeted geographic cells during orbital transit passes rather than continuous 24/7 connectivity. Nevertheless, establishing functional D2D data and voice links marks a pivotal milestone for emergency communications and remote rural coverage.

Carrier Ecosystem: AT&T, Verizon, and Global Partners

AST SpaceMobile’s commercial strategy relies heavily on deep integration with Mobile Network Operators (MNOs) rather than operating as an independent retail carrier. In the United States, the company maintains high-profile strategic partnerships with AT&T and Verizon [cite: 2.1.5], alongside international alliances with Vodafone, Rakuten Mobile, and Bell Canada [cite: 2.1.5].

These partnerships allow partner carriers to offer satellite roaming directly to existing subscribers when terrestrial towers are out of reach. Recent FCC regulatory approvals clearing low-earth orbit satellite operations across specific low-band spectrum frequencies [cite: 2.1.5] have positioned the company to conduct rigorous live network testing in coordination with AT&T and FirstNet infrastructure [cite: 2.1.5].

Competitive Landscape: SpaceX Starlink and Spectrum Battles

The race to dominate space-based cellular broadband is intensifying across the US technology sector. SpaceX continues to advance its Starlink direct-to-cell initiatives, recently pursuing strategic low-band spectrum acquisitions to bolster its carrier ambitions [cite: 2.1.5]. Simultaneously, major global telecom consortia are evaluating joint bids for upcoming satellite spectrum allocations [cite: 2.1.5].

Industry experts emphasize that regulatory approvals, spectrum availability, and launch cadence will dictate market leadership over the next several years. While SpaceX boasts an established rocket launch infrastructure, AST SpaceMobile’s large-aperture satellite design has earned praise from carrier partners for delivering high-bandwidth cellular signals directly to standard phones.

What US Consumers Can Expect by Year-End

As AST SpaceMobile approaches its year-end target for initial US deployment [cite: 2.1.5], subscribers on partner networks like AT&T and Verizon should anticipate phased rollouts focusing on emergency text messaging and basic data services in designated test regions.

As additional LEO satellites launch into orbit throughout 2027, intermittent coverage windows will transition into seamless, continuous connectivity, effectively eliminating cellular dead zones across national highways, national parks, and rural communities.

Frequently Asked Questions

Q: What is satellite D2D connectivity? Direct-to-device (D2D) technology allows standard, unmodified mobile phones to connect directly to satellites in orbit for voice and data services [cite: 2.1.5].

Q: When will US users see coverage? AST SpaceMobile announced plans for initial, intermittent coverage in the US, Canada, Japan, and other regions by the end of 2026 [cite: 2.1.5].

Q: Which carriers support the network? The company partners with major tier-one operators including AT&T, Verizon, and Vodafone [cite: 2.1.5].

Conclusion

AST SpaceMobile’s progress toward initial US satellite D2D coverage highlights the rapid convergence of space exploration and telecommunications. By partnering with major US carriers to connect standard smartphones via orbit, the industry is poised to eradicate cellular dead zones once and for all.

Sources

Reference 1: • Light Reading (October 21, 2026): ‘AST SpaceMobile limited coverage coming soon in US and beyond’ – https://www.lightreading.com/satellite/ast-spacemobile-says-limited-coverage-coming-soon-in-us-and-beyond [cite: 2.1.5]

The Cybersecurity and Infrastructure Security Agency (CISA) issued a federal alert on October 20, 2026, adding six newly discovered security flaws to its authoritative Known Exploited Vulnerabilities (KEV) Catalog [cite: 1.4.1]. Based on conclusive evidence confirming active exploitation in the wild, the emergency addition mandates that federal agencies and commercial enterprise networks remediate the vulnerabilities within specified statutory timeframes [cite: 1.4.1]. The latest inclusions span popular media server software, industrial automation tools, and enterprise security platforms.

Breaking Down the Six Newly Added Vulnerabilities

The October 20 catalog update highlights diverse attack surfaces exploited by threat actors across global networks. Among the notable entries are two distinct flaws affecting Plex Media Server: CVE-2026-96652, a Server-Side Request Forgery (SSRF) vulnerability, and CVE-2026-96656, which involves external control of file names or paths [cite: 1.4.1]. These flaws allow remote attackers to interact with internal network resources or manipulate server file directories if left unpatched.

Additionally, CISA flagged CVE-2026-106931, an OS command injection vulnerability impacting EG Secure Solutions SiteGuard Server Edition, and CVE-2026-110936, an uncontrolled search path element vulnerability within Siemens Software Center [cite: 1.4.1]. The remaining entries address active exploitation vectors targeting enterprise administrative interfaces and file-handling utilities, underscoring the relentless persistence of cyber adversaries targeting edge infrastructure.

Why the KEV Catalog Drives Enterprise Defense

Established under Binding Operational Directive (BOD) 22-01, CISA’s KEV Catalog serves as the gold standard for prioritizing vulnerability management across public and private sectors. While software vendors publish thousands of Common Vulnerabilities and Exposures (CVEs) annually, security teams frequently struggle to determine which flaws demand immediate patching.

By explicitly flagging vulnerabilities confirmed to be under active exploitation by malicious actors, CISA provides organizations with actionable intelligence. Federal civilian executive branch (FCEB) agencies are legally required to remediate KEV items within strict deadlines, while commercial enterprises increasingly adopt the catalog as a baseline benchmark for risk prioritization.

Technical Analysis of SSRF and Command Injection Vectors

The inclusion of Server-Side Request Forgery and OS command injection flaws underscores recurring architectural risks in complex software applications. SSRF vulnerabilities occur when an application fails to validate user-supplied input before initiating remote HTTP requests, enabling attackers to query internal metadata services or restricted local network segments.

Similarly, command injection allows unauthenticated or privileged adversaries to execute arbitrary system commands directly on the host operating system. Cybersecurity analysts emphasize that threat actors frequently weaponize these flaws within hours of public disclosure, automating scanning and exploitation scripts across exposed internet-facing assets.

Actionable Mitigation Steps for IT Security Teams

In response to the catalog update, enterprise security teams must immediately inventory their software assets to identify instances of Plex Media Server, Siemens Software Center, and SiteGuard Server Edition. Applying vendor-supplied patches or implementing temporary network segmentation controls is critical to neutralizing active exploit chains.

CISA continues to urge all organizations—regardless of sector—to integrate the KEV catalog into their automated vulnerability scanning workflows and patch management pipelines.

Frequently Asked Questions

Q: What is the CISA KEV Catalog? The KEV Catalog is a CISA-maintained database tracking software vulnerabilities with confirmed evidence of active exploitation in the wild [cite: 1.4.1].

Q: What was included in the October 20 update? CISA added six new vulnerabilities on October 20, 2026, including flaws in Plex Media Server, Siemens Software Center, and SiteGuard Server Edition [cite: 1.4.1].

Q: How should organizations respond? Organizations should apply official vendor patches immediately, review access controls, and monitor network logs for suspicious requests.

Conclusion

CISA’s addition of six active exploitation flaws to the KEV catalog serves as a vital reminder of the speed at which threat actors weaponize software vulnerabilities. Prompt patching and rigorous vulnerability management remain the cornerstone of robust enterprise cybersecurity.

Sources

Reference 1: • Cybersecurity and Infrastructure Security Agency (CISA) Alerts (October 20, 2026): ‘CISA Adds Six Known Exploited Vulnerabilities to Catalog’ – https://www.cisa.gov/news-events/alerts/2026/10/20/cisa-adds-six-known-exploited-vulnerabilities-catalog [cite: 1.4.1]

In a significant milestone for infectious disease medicine, the U.S. Food and Drug Administration (FDA) officially approved Hibsago (bepirovirsen) injection on October 20, 2026 [cite: 1.3.2]. Developed by GSK, Hibsago is approved for use in combination with existing nucleoside analog antiviral therapy for adults suffering from chronic hepatitis B [cite: 1.3.1]. Representing a first-of-its-kind therapeutic approach [cite: 1.3.2], the approval offers renewed hope for millions of patients worldwide by introducing a mechanism designed to achieve a functional cure rather than lifelong viral suppression alone.

Understanding Chronic Hepatitis B and Treatment Challenges

Chronic hepatitis B is a persistent viral infection affecting the liver, capable of leading to severe complications including cirrhosis, liver failure, and hepatocellular carcinoma. Standard care traditionally relies on long-term nucleoside analog (NA) therapies that suppress viral replication effectively but rarely eradicate the surface antigen (HBsAg) or achieve a sustained functional cure, requiring patients to maintain continuous lifelong medication regimens.

Bepirovirsen, the active pharmaceutical ingredient in Hibsago, is an antisense oligonucleotide designed to target hepatitis B virus (HBV) messenger RNA. By binding to viral RNA transcripts, the drug inhibits viral protein synthesis and reduces the production of hepatitis B surface antigen, enabling the patient’s immune system to mount an effective defense against the persistent virus.

Clinical Trial Results and Phase 3 Data

The FDA approval was anchored by robust data from pivotal Phase 3 clinical trials evaluating finite courses of bepirovirsen in combination with existing nucleoside therapies [cite: 1.3.1]. Trial findings demonstrated that a meaningful percentage of patients—specifically 19% [cite: 1.3.1]—achieved a functional cure, defined as the sustained loss of hepatitis B surface antigen and undetectable HBV DNA for at least 24 weeks following treatment discontinuation [cite: 1.3.3].

Medical researchers note that achieving a functional cure allows patients to stop antiviral therapy safely without experiencing viral relapse, a breakthrough that transforms clinical management paradigms for chronic liver disease specialists across the United States.

Access, Pricing, and US Market Rollout

Following the federal approval, GSK announced plans to roll out Hibsago across US specialty pharmacies and hepatology clinics. Healthcare economists point out that while innovative specialty therapeutics offer immense clinical value, launch pricing and insurance formulary coverage remain critical factors for patient access.

Recent industry reports highlight that median net launch prices for breakthrough specialty medications have risen steadily over recent years, prompting payers to implement prior authorization criteria and step-therapy protocols. Gastroenterologists and hepatologists anticipate working closely with insurance providers to establish clear coverage pathways for eligible adult patients.

What This Means for Patients and Providers

For practicing physicians, Hibsago provides an essential new therapeutic tool to alter the natural history of chronic hepatitis B. Patients who previously faced decades of daily maintenance medication now have access to a finite treatment course with demonstrated potential for immune control.

Medical centers across the US are updating clinical care protocols to incorporate bepirovirsen into treatment algorithms, emphasizing patient screening and baseline biomarker evaluations.

Frequently Asked Questions

Q: What is Hibsago? Hibsago (bepirovirsen) is an FDA-approved antisense oligonucleotide injection used alongside existing antiviral therapy for adults with chronic hepatitis B [cite: 1.3.1, 1.3.2].

Q: What clinical results supported the approval? Phase 3 clinical trials demonstrated a 19% functional cure rate, defined as sustained surface antigen loss and undetectable viral DNA after treatment discontinuation [cite: 1.3.1, 1.3.3].

Q: How is the treatment administered? It is administered as an injection in combination with ongoing nucleoside analog therapy under specialist supervision [cite: 1.3.2].

Medical Disclaimer

Note: This article is for informational and educational news reporting purposes only and does not constitute medical advice, diagnosis, or treatment recommendations. Patients should consult qualified healthcare providers for medical guidance.

Conclusion

The FDA approval of Hibsago represents a major milestone in hepatitis B therapeutics, offering a validated path toward functional cure for chronic patients. As GSK deploys the treatment across US medical markets, clinical practice will increasingly embrace finite, immune-targeted therapeutic strategies.

Sources

Reference 1: • U.S. Food and Drug Administration (FDA) Press Announcements (October 20, 2026): ‘FDA Approves First-of-Its-Kind Chronic Hepatitis B Treatment’ – https://www.fda.gov/news-events/press-announcements/fda-approves-first-its-kind-chronic-hepatitis-b-treatment [cite: 1.3.2]

Reference 2: • Pharmaceutical Executive Daily (October 21, 2026): ‘FDA Approves Hibsago (Bepirovirsen) for Chronic Hepatitis B’ – https://www.pharmexec.com/view/daily-fda-approves-hibsago [cite: 1.3.1]

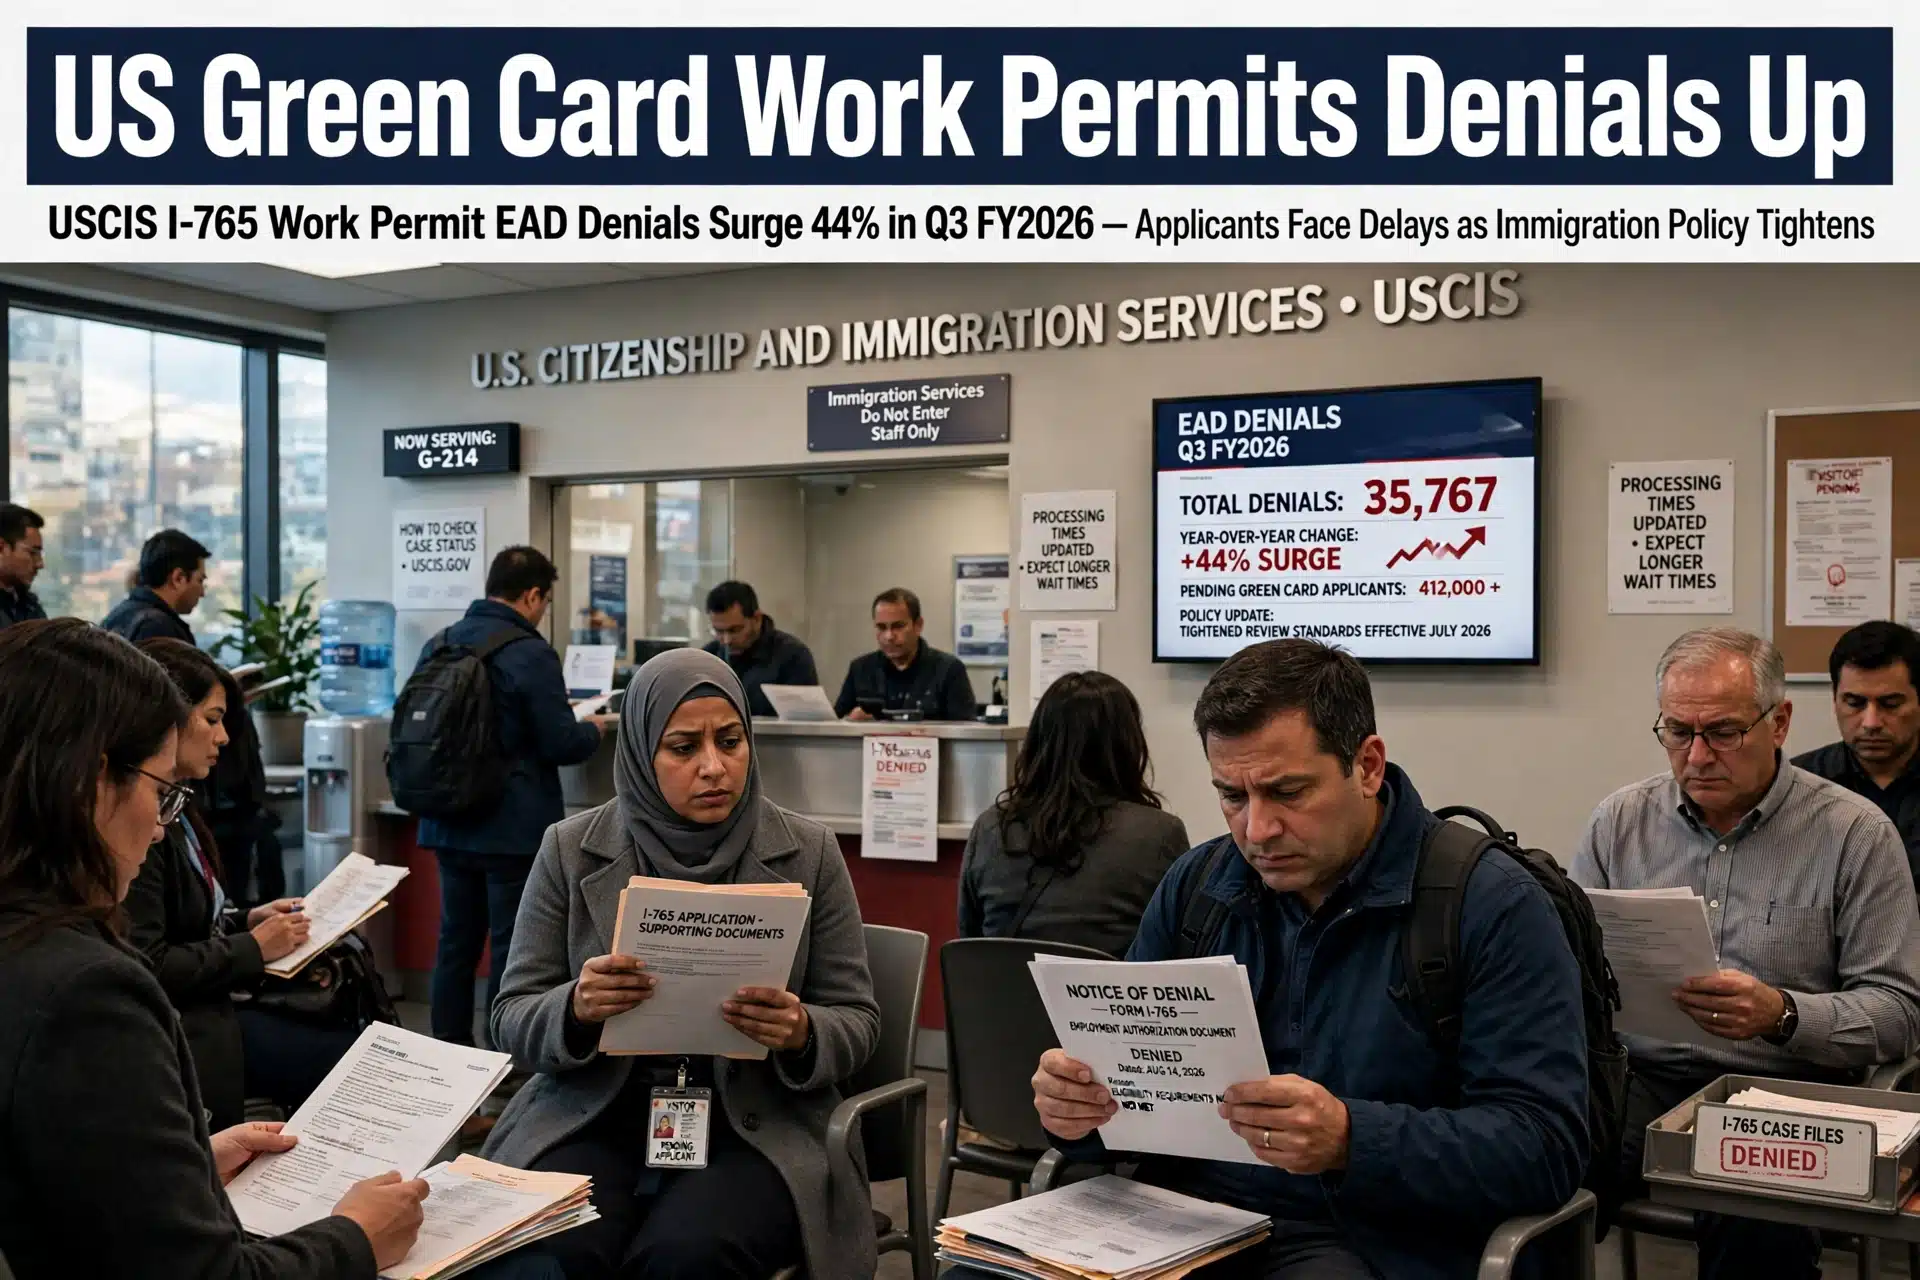
Data released by United States Citizenship and Immigration Services (USCIS) covering the third quarter of the 2026 fiscal year highlights a dramatic tightening of employment authorization adjudications [cite: 1.2.1]. Foreign nationals seeking permanent residency in the US experienced a sharp surge in work permit denials, with rejection rates climbing to approximately 44% between April and June 2026 [cite: 1.2.1]. This escalation represents a significant jump from the 25% rejection average recorded during the first half of the fiscal year, placing intense pressure on international professionals, corporate employers, and legal practitioners navigating the adjustment-of-status pipeline.

Analyzing the Q3 USCIS Adjudication Numbers

According to official figures analyzed across government filings, USCIS received 153,039 applications under Form I-765 (Application for Employment Authorization) through the adjustment-of-status category during the April-June quarter [cite: 1.2.1]. Out of this total volume, the agency approved 46,405 applications while issuing 35,767 formal rejections [cite: 1.2.1]. The remaining applications continued working through administrative processing queues.

The sudden spike in denials has alarmed immigration attorneys and human resources departments across the United States. Many applicants who rely on Employment Authorization Documents (EADs) to maintain continuous employment while their Green Card petitions remain pending face unexpected disruptions. Compounding the issue, the total backlog of pending Form I-765 adjustment-of-status applications stood at 671,362, with standard processing times averaging 6.4 months [cite: 1.2.1].

Impact Across H-1B and Employment-Based Petitions

The stricter adjudication trends extended well beyond adjustment-of-status work permits. Temporary foreign worker petitions filed under Form I-129—which encompasses H-1B specialty occupation visas—recorded 39,560 denials against 143,748 approvals, resulting in an overall rejection rate of approximately 22% [cite: 1.2.1].

Similarly, employment-based immigrant worker petitions submitted via Form I-140 registered 7,069 denials and 37,975 approvals, representing a 16% rejection rate [cite: 1.2.1]. Family-based immigration petitions filed under Form I-130 saw 16,661 rejections, accounting for roughly 17% of total adjudications [cite: 1.2.1]. Industry experts note that heightened scrutiny on evidentiary standards, specialized role definitions, and wage level justifications are driving the elevated denial figures.

Why Are Rejection Rates Climbing in 2026?

Immigration analysts point to several contributing factors behind the tightening approval criteria. Federal adjudicators have adopted more rigorous compliance checks regarding employer-employee relationships, specialized knowledge documentation, and maintenance of lawful status prior to filing. Furthermore, operational backlogs have pushed adjudicating officers to apply stricter initial review thresholds.

For corporate employers hiring international talent, these trends necessitate enhanced legal preparation. Submitting comprehensive documentation at the initial filing stage is critical to avoiding Requests for Evidence (RFEs) or outright denials that can derail project staffing and employee retention plans.

Strategic Advice for Employers and Applicants

In light of the 44% EAD rejection rate, legal counsel recommends filing renewal applications well in advance of current expiration dates. Under current federal regulations, eligible applicants should review automatic extension provisions where applicable, though relying on extensions requires careful tracking of regulatory limits.

Employers sponsoring foreign nationals should conduct thorough internal audits of job descriptions, prevailing wage determinations, and corporate compliance records to withstand heightened federal scrutiny.

Frequently Asked Questions

Q: What is a green card work permit (Form I-765)? Form I-765 allows eligible foreign nationals seeking permanent residency to obtain an Employment Authorization Document (EAD) to work legally while their green card is processed [cite: 1.2.1].

Q: How high did the rejection rate climb? USCIS rejection rates for adjustment-of-status EAD applications climbed to approximately 44% during the April–June 2026 quarter [cite: 1.2.1].

Q: What steps can applicants take to mitigate risks? Applicants should file renewals well ahead of deadlines, ensure airtight supporting documentation, and consult qualified immigration counsel.

Disclaimer

Note: This article is for informational news reporting purposes only and does not constitute legal or immigration advice. Readers should consult a licensed immigration attorney for specific case evaluations.

Conclusion

The latest USCIS adjudication statistics underscore an increasingly challenging regulatory environment for foreign nationals and US employers. With work permit denial rates reaching 44% and massive backlogs persisting, proactive compliance and meticulous legal preparation are more essential than ever for navigating the US immigration system.

Sources

Reference 1: • Free Press Journal / Financial Express Reporting (October 15, 2026): ‘US Rejects Over 35,000 Green Card Applicants’ Work Permits As Denial Rate Jumps To 44 Per Cent’ – https://www.freepressjournal.in/world/us-rejects-over-35000-green-card-applicants-work-permits-as-denial-rate-jumps-to-44-per-cent [cite: 1.2.1]

Reference 2: • Live Mint Reporting (October 16, 2026): ‘US immigration fees rise effective today: Will H-1B workers, students and green card applicants from India pay more?’ – https://www.livemint.com/news/india/us-immigration-fees-rise-effective-today-will-h-1b-workers-students-and-green-card-applicants-from-india-pay-more-11792130925700.html [cite: 1.2.2]

On October 21, 2026, a consortium comprising T-Mobile, Nokia, and NVIDIA announced a breakthrough in telecommunications infrastructure: the successful execution of the world’s first AI-RAN (Artificial Intelligence Radio Access Network) call on a live commercial network in Bellevue, Washington [cite: 2.1.1]. Operating over T-Mobile’s production 5G Standalone (SA) core using a standard commercial smartphone, this milestone marks the transition of artificial intelligence from closed laboratory environments into active, everyday cellular infrastructure [cite: 2.1.1]. For US consumers and enterprise networks alike, this convergence of radio frequency engineering and neural network inference promises to redefine how mobile data and real-time compute interact across the country.

What Is an AI-RAN and Why Does It Matter for US 5G?

Traditional telecommunications architecture treats cellular base stations and data centers as separate entities. Cell towers handle radio waves, demodulating signals and passing raw data packets back through regional gateways to centralized cloud servers for processing. This separation introduces latency and requires redundant hardware investments. An AI-RAN architecture fundamentally alters this paradigm by embedding powerful accelerated computing directly into the radio access network site.

During the Bellevue test, Nokia’s commercial base station hardware powered by NVIDIA accelerated computing platforms ran both standard 5G wireless protocol stacks and real-time AI inference workloads simultaneously on the same silicon. This dual-use capability enables cell towers to act as localized edge computing nodes. For US subscribers, the immediate benefit is reduced latency for latency-sensitive applications such as autonomous vehicle coordination, augmented reality headsets, and immersive cloud gaming, while carriers eliminate the need for costly parallel infrastructure builds.

Inside the Bellevue Deployment: Technical Architecture

The technical achievement required rigorous synchronization between radio frequency (RF) timing and high-throughput parallel processing. In a conventional cellular deployment, peak capacity must be provisioned to handle maximum potential user demand, leading to underutilized hardware during off-peak hours. By integrating AI inference engines directly into the RAN, the network can dynamically reallocate computational resources between telecommunications routing and edge AI tasks.

Industry analysts following the announcement note that this architecture allows mobile operators to monetize their real estate. With thousands of macro towers and small cell sites distributed across US metropolitan and rural areas, carriers possess an unparalleled distributed physical footprint. Transforming these sites into intelligent compute hubs opens new revenue streams for enterprise edge services, smart city telemetry, and localized industrial automation without requiring clients to route data back to distant hyperscale data centers.

Industry Implications: NVIDIA, Nokia, and Carrier Competition

The collaboration highlights an intensifying race among hardware manufacturers and infrastructure vendors to dominate next-generation telecom standards. While NVIDIA continues to expand its footprint from enterprise data centers into telecommunications infrastructure, legacy equipment makers like Nokia are pivoting aggressively toward software-defined networking and virtualized RAN (vRAN) frameworks.

For T-Mobile, early deployment on a live production core demonstrates a strategic commitment to network modernization following its nationwide 5G Standalone rollout. Competitors across the US telecom sector are closely evaluating the trial results to determine capital expenditure timelines. As data consumption driven by generative AI applications surges across mobile devices, carriers face mounting pressure to optimize spectral efficiency and reduce power consumption per gigabit transmitted.

What Happens Next for US Mobile Subscribers?

While everyday smartphone users will not immediately notice a visual change in their signal bars, the backend transformation will gradually manifest in improved reliability during network congestion and faster response times for cloud-connected services. Enterprises building localized IoT deployments can expect greater support for edge processing directly through carrier partnerships.

As Nokia and NVIDIA prepare to scale AI-RAN deployment kits for broader carrier adoption into 2027, the focus will shift toward software ecosystem maturity, multi-vendor interoperability, and stringent cybersecurity standards for distributed network nodes.

Frequently Asked Questions

Q: What is an AI-RAN call? An AI-RAN (Artificial Intelligence Radio Access Network) integrates AI compute directly into cellular base stations, allowing the same hardware to handle radio signals and AI tasks simultaneously.

Q: Where did the milestone test occur? It took place on October 21, 2026, at a live commercial cell site in Bellevue, Washington, on T-Mobile’s production 5G network [cite: 2.1.1].

Q: How does this benefit everyday mobile users? It significantly reduces latency, optimizes cellular spectral efficiency, and turns cell towers into localized edge computing nodes for advanced applications.

Conclusion

The successful execution of the first US AI-RAN call marks a pivotal turning point for the telecommunications industry. By proving that cellular infrastructure and artificial intelligence can share processing workloads efficiently on live networks, T-Mobile, Nokia, and NVIDIA have established a blueprint for the future of connectivity. As adoption expands across the US, the integration of intelligent computing into the network core will redefine digital capabilities for consumers and enterprises alike.

Sources

Reference 1: • NVIDIA Newsroom (October 21, 2026): ‘NVIDIA, Nokia and Leading Telecom Operators Turn Networks Into Distributed Intelligence Platforms’ – https://nvidianews.nvidia.com/news/nvidia-nokia-and-leading-telecom-operators-turn-networks-into-distributed-intelligence-platforms [cite: 2.1.2]

Reference 2: • Shattered.io Tech Reporting (October 21, 2026): ‘T-Mobile’s AI-RAN Call Pulls In 3 More Carriers’ – https://shattered.io/t-mobile-ai-ran-call-pulls-3-carriers-2026/ [cite: 2.1.1]

Note: this article is informational and is not legal advice; filing questions that affect a specific case should go to an immigration attorney or an accredited representative before the deadline.

USCIS Changes How Filing Deadlines Count, Starting Friday October 23

USCIS filing deadlines change on Friday, October 23, 2026, when Policy Alert PA-2026-15 takes effect and redraws, in a narrow but consequential way, which deadlines get a weekend cushion and which do not. For qualifying paper filings whose deadlines are counted in days, a deadline falling on a Saturday, Sunday or federal holiday can roll forward to the next business day. Age-based eligibility cutoffs do not roll, and electronically filed requests never get the extension at all, because USCIS treats them as received the moment they are submitted. The alert, issued September 23, reverses the broader 2023 treatment of certain eligibility cutoffs, so applicants, employers and attorneys who built habits under the old rules need one working week to adjust.

Key Takeaways:

  • – PA-2026-15 takes effect October 23, 2026 and applies to paper-based filings received on or after that date.
  • – For qualifying deadlines expressed in days, calendar days include weekends and holidays, and the next-business-day rule applies when the last day falls on a weekend or holiday.
  • – Substantive eligibility cutoffs, like filing while under 21, are not extended; the alert itself uses a Special Immigrant Juvenile Form I-360 example.
  • – Electronic filings are received immediately on submission, so the weekend-and-holiday extension never applies online.
  • – A rejected filing does not keep a filing date, and a delivery scan alone does not prove a filing met the requirements.

The Rule in Plain Language: Three Deadline Types

USCIS has always used different clocks for different deadlines, and PA-2026-15 makes the differences harder to blunder into. For a qualifying day-count period attached to a paper filing, calendar days count weekends and holidays, and when the final day is a non-business day, a paper receipt by the end of the next business day can still be timely; the regulatory anchor is the definition of day in 8 CFR 1.2. For an age-carrying or otherwise substantive eligibility condition, nothing moves: a petitioner required to be under 21 at filing does not buy an extra three days because the 21st birthday lands on a Saturday. For anything filed electronically, the weekend-and-holiday extension is off the table, since the online system timestamps receipt instantly, and an unfinished draft sitting in a USCIS online account is not a submission.

Why USCIS Changed Course Now

The alert’s stated reason is conformity with case law and with the regulatory definition of day, per the policy-alert text AILA published in full. Its practical effect is to end the ambiguity that 2023-era guidance created on eligibility cutoffs, precisely the ambiguity that produces rejected filings and lost eligibility. From an agency operations view, the change also aligns the paper and electronic worlds: online filers never had a weekend cushion, so narrowing the paper cushion to day-count deadlines only removes a discrepancy between two filing channels that increasingly share adjudication infrastructure. Immigration-law commentators flagged the reversal risk early: VisaVerge’s coverage summarized the end of the next-business-day extension for online filings, and Herman Legal Group’s October 20 explainer, checked against the alert that same day, walks through both directions with worked examples.

Two Worked Examples That Show the Trap

The clearest way to see the stakes is with the two scenarios the coverage models. First, a paper RFE response whose day-count deadline lands on Sunday, October 25: if the governing deadline qualifies and Monday, October 26 is a business day, USCIS receiving the response on Monday can still be timely, but dropping the package in the mail on Monday is not the same as USCIS receiving it, since the general receipt rule under 8 CFR 103.2(a)(7) keys to actual receipt at the designated filing location. Second, a Special Immigrant Juvenile petitioner who turns 21 on a Saturday: under PA-2026-15, the weekend does not preserve eligibility until Monday, so the working plan must be USCIS receipt before the weekend. Those two examples, one day-count and one age-cutoff, are the entire policy in miniature, and filing teams that memorize the distinction will not need the rest of the alert.

What This Means for Employers and HR Teams

Employers have the most mechanically exposed calendars, because H-1B changes of status, I-9-adjacent timelines and PERM-adjacent responses all run on day-count clocks, and October-to-January is peak federal-holiday season. The immediate moves: audit every open USCIS case for deadlines that fall within the next 60 days; check whether any response window is expressed as a number of days rather than fixed by a notice date; and for anything filed electronically, treat the platform timestamp as absolute. HR teams should also refresh the advice they give to foreign-national employees, because the single most dangerous misread of PA-2026-15 is a missed RFE or NOID response followed by a denial that then requires costlier motion practice. The fix costs one calendar annotation per case; the miss costs the case.

What the Rule Does Not Do

Scope discipline matters here, because coverage of the alert has already produced headline-level misreads. PA-2026-15 is a filing-computation rule, not a general extension of anyone’s status, work authorization or travel window. It does not change immigration court or BIA deadlines, consular processing timelines, or the separate CSPA age-protection math, and the alert itself cautions that some benefits, including certain asylum procedures, follow different regulations entirely. The rejection rule also cuts in a direction filers sometimes forget: under the general receipt rule, a rejected benefit request does not retain a filing date, and a delivery scan alone does not establish that the request satisfied the filing requirements, so form edition, signature, fee and initial evidence all matter independently of when the packet arrived.

What Happens Next

Two follow-on pressures are predictable. First, USCIS will publish the revised Policy Manual text and practitioners will discover edge cases, forms whose instructions embed their own deadline definitions and rejections issued in the first week under the new clock, so watch for early-hit reports from the immigration bar; feedback on the alert was due October 23 as well, meaning the agency heard the profession’s objections in real time. Second, the Monday-receipt scenarios will concentrate hard in this window, because November contains Thanksgiving-week federal holidays and December contains the winter holidays, so the paper-deadline roll-forward will be live within days of the policy’s first week. Workers and applicants: the practical answer is not to test the rule at all. File early, keep the delivery confirmation, and treat every deadline as one business day earlier than printed, because under the new math Friday is already Monday’s twin.

Frequently Asked Questions

Do USCIS deadlines still extend over a weekend?

For qualifying paper filing deadlines counted in days, yes: if the last day falls on a weekend or federal holiday, receipt by the end of the next business day can be timely. The extension does not apply to eligibility cutoffs or to electronically filed requests.

Does the October 23 rule affect online filings?

Electronically submitted benefit requests are treated as received immediately at submission, so the weekend-and-holiday extension never applies online, and an unfinished draft in a USCIS online account is not a completed filing.

Does a weekend birthday preserve my eligibility until Monday?

No. Under PA-2026-15, substantive eligibility cutoffs such as filing while under 21 are not extended; plan for USCIS to receive the filing before the birthday, not after it.

Sources:

https://www.visaverge.com/documentation/uscis-ends-next-business-day-extension-for-online-filings-under-policy-alert-pa-2026-15

Romanian F-16s Down Two Russian-Style Geran Drones as NATO Heads Into Black Sea Talks

The Romania drone shootdown happened Saturday evening, when two Romanian air force F-16s destroyed a pair of Geran attack drones over the country’s territorial waters in the Black Sea after the fast-moving aircraft crossed into Romanian airspace. The encounter, confirmed by Romania’s defense ministry and covered by Stars and Stripes on October 19, is the sharpest sign yet of a widening Black Sea crisis that brings the alliance’s top decision-making body to Brussels this Tuesday for urgent talks on expanding NATO’s military presence and surveillance in the region. For US readers, the stakes are straightforward: an American-led alliance is now routinely shooting war hardware out of NATO skies.

Key Takeaways:

  • – Two Romanian F-16s shot down two Geran attack drones Saturday over Romanian territorial waters; the drones were traveling roughly 280 mph.
  • – Romania has logged 35 unauthorized drone incursions in 2026, up from nine in 2025, and shot down six drones this year after none last year.
  • – The North Atlantic Council meets Tuesday in Brussels to discuss expanding NATO’s Black Sea presence and surveillance, per Romanian Foreign Minister Oana Toiu.
  • – Several commercial vessels have been attacked near Romania and Bulgaria in recent weeks, with sailors killed or missing and no official attribution yet.
  • – Bulgaria has requested additional allied aircraft and counter-drone capabilities.

What Happened Saturday, Minute by Minute

The sequence reconstructed from ministry statements and reporting is short. Romanian radar picked up the drones approaching national airspace from the Black Sea, F-16s on alert scrambled, and the intercepts came at 6:01 PM and 6:05 PM near Sulina, at the mouth of the Danube, above territorial waters. The aircraft were Geran attack drones, the Russian-associated loitering munition family now flying at roughly 280 miles per hour, fast enough that jet-powered propulsion rather than propeller drive is the practical inference, a hardware upgrade United24’s war desk flagged in its coverage of the incident. Scrap photography from the intercept site circulated within a day. The ministry’s statement afterward emphasized that the military continuously adapts procedures and response measures to defend airspace and territorial waters, which in official language means Romanian crews are now running live intercept drills as a standing mission rather than a novelty.

The Numbers That Changed This Year

The statistical jump is the story. Romania recorded 35 unauthorized drone incursions in 2026 against nine in 2025, roughly a fourfold increase, and Romanian forces downed six drones this year after shooting none down the previous year. Explanations divide into three: Russia’s air campaign against Ukraine’s ports and infrastructure drives more hardware westward toward NATO territory; the drones themselves got faster and longer-ranged; and Romanian detection and engagement doctrine matured, so more incursions are now tracked and shot rather than unnoticed. None of the three explanations are mutually exclusive, and all three point the same direction, which is why the alliance moved from watching to convening.

What NATO Is Actually Deciding Tuesday

The North Atlantic Council, the alliance’s top body, meets at NATO headquarters in Brussels on Tuesday, and Romanian Foreign Minister Oana Toiu laid out the agenda on Romanian television Sunday: how to expand the alliance’s military presence in the Black Sea region and increase surveillance capabilities. Bulgaria has already requested additional allied aircraft and counter-drone systems. Secretary-General Mark Rutte met Romanian President Nicusor Dan and Bulgarian Prime Minister Rumen Radev last week and said afterward that the alliance strengthened its eastern flank posture and would continue adjusting defenses. The genuinely hard problem, as Stripes’ reporting notes, lies outside alliance territory: drone and missile attacks on commercial shipping in international waters near Romania and Bulgaria, where numerous sailors have been killed or remain missing, investigations continue, and no official blame has been made public. NATO’s charter obligations run to alliance territory, not to neutral merchant ships, so the practical lever on shipping attacks is surveillance, convoying and national self-defense rather than Article 5.

The Black Sea pattern connects to a wider sabotage campaign US readers rarely see in one frame. Lithuanian authorities said Sunday that suspected saboteurs attempted to set fire to a facility housing SpaceX Starlink communications equipment near Vilnius, with the country’s National Crisis Management Center linking the incident to Russian efforts to disrupt Ukraine’s military communications. That attempted arson follows other attacks on Starlink facilities in Poland and Bulgaria this year, and Polish authorities have blamed Russia for a September attack on a Polish installation, with suspects detained in Germany. The through-line is deliberate: degrade whichever network, logistics node or sensor tracks and intercepts the drones. It also explains the Geran upgrade cycle, since a 280-mph jet-propelled drone exists precisely to exhaust defender missiles and response windows, a design trade that has now landed on NATO’s own intercept docket.

Why US Taxpayers and Shoppers Should Care

The material connection is air defense economics, not symbolism. Each F-16 intercept burns fuel, airframe hours and, in many NATO cases, expensive missiles at targets costing a fraction of the interceptor, a cost-per-kill asymmetry Russia’s drone designers exploit deliberately. The US has quietly backed Romania’s western Black Sea radar integration and contributed aircraft rotations, because a contested Black Sea is a global grain-export and energy-transit choke point: shipping insurance rates and freight costs trace the drone war directly into American food and fuel prices. And with Lithuania now reporting attacks on Starlink-linked infrastructure, US commercial satellite hardware is inside the conflict, which raises both the insurance question and the question of when privately owned infrastructure gets military protection.

What Happens Next

Watch three deliverables from Tuesday’s council meeting. A reinforced air-and-ISR package for Bulgaria and Romania, likely fighter detachments plus counter-drone systems and expanded radar coverage, is the cheapest consensus outcome. A shared attribution framework for the shipping attacks, where allied navies publish forensic findings jointly rather than letting each capital hedge, would mark a real policy shift. And the dry-run risk: the next Geran incursion that strays deeper than Sulina, toward a populated Romanian area, forces a NATO-vs-Russia decision inside a 90-second engagement window, which is exactly the scenario the alliance hopes expanded surveillance prevents. The path from here runs through Brussels this week; the alternative is more Saturdays like this one, with allied jets over the Danube delta and scrap raining into the reeds.

Frequently Asked Questions

Why did Romania shoot down the drones?

Two Geran attack drones approached from the Black Sea and entered Romanian airspace; F-16s scrambled and destroyed them over territorial waters near Sulina, at 6:01 PM and 6:05 PM Saturday.

How many drones entered Romanian airspace in 2026?

Romania logged 35 unauthorized drone incursions in 2026, compared with nine in 2025, and shot down six drones this year after none last year.

What will NATO decide in the Tuesday talks?

The North Atlantic Council meets in Brussels to discuss expanding NATO’s Black Sea military presence and surveillance, against the backdrop of Bulgaria’s request for more allied aircraft and counter-drone capabilities and ongoing attacks on commercial shipping nearby.

Sources:

Note: this article is informational and is not medical advice; treatment decisions belong with a hepatologist who can review liver labs, viral load and individual risk.

FDA Approves Hibsago, the First Treatment Aimed at a Functional Cure for Hepatitis B

The Hibsago FDA approval arrived on October 20, 2026, when GSK announced that the agency had cleared bepirovirsen for chronic hepatitis B, the first therapeutic aimed squarely at a functional cure rather than lifelong viral suppression for eligible patients. The drug is approved for adults without cirrhosis who are already on at least six months of nucleos(t)ide analog therapy with suppressed HBV DNA and whose surface antigen (HBsAg) level is at or below 3,000 IU/mL on an FDA-authorized test. About 1.7 million people in the United States live with chronic hepatitis B, and until now the standard of care suppresses the virus indefinitely without clearing it.

Key Takeaways:

  • – FDA approved Hibsago (bepirovirsen) on October 20, 2026 for adults without cirrhosis on NrtI therapy for at least six months with suppressed HBV DNA and HBsAg at 3,000 IU/mL or below.
  • – In pooled phase 3 B-Well data, 19% of treated adults (233 of 1,220) achieved a functional cure versus none of the placebo arm; the standard of care alone typically achieves under 1% after a year.
  • – Among patients with HBsAg at or below 1,000 IU/mL, roughly 45% of diagnosed cases globally, the functional-cure rate was 26%.
  • – The drug carries a boxed warning for on-treatment hepatic flares and thrombocytopenia, with platelet and liver-enzyme monitoring required throughout.
  • – A six-month course is given by injection, with the option of self-administration after the first dose.

What the B-Well Trial Data Shows

The approval rests on the pooled B-Well phase 3 program: two global, randomized, double-blind, placebo-controlled trials across 29 countries. Six months of bepirovirsen achieved a functional-cure rate of 19%, 233 of 1,220 participants, against 0 of 614 on placebo. Functional cure, the marker the whole field chases, is defined as undetectable HBV DNA and undetectable HBsAg for at least 24 weeks after stopping all treatment, meaning the immune system holds the disease down on its own. Depth of response tracked baseline surface antigen levels: at 1,000 IU/mL or below, 26% achieved functional cure (200 of 768), and exploratory analyses showed 49% of the overall population reached HBsAg levels of 100 IU/mL or under by week 72, a range associated in the medical literature with better immune control. Safety coverage matters for context: chronic hepatitis B accounts for roughly 56% of all liver cancer cases worldwide, so any therapy that durably clears surface antigen has cancer-prevention stakes, a case the Hepatitis B Foundation underscored in welcoming the decision.

Who Actually Qualifies

The label carve-outs are strict, and they define the drug’s practical reach. Hibsago is only for adults without cirrhosis, on nucleos(t)ide therapy for at least six months, with fully suppressed HBV DNA, and with measured HBsAg at or below 3,000 IU/mL using an FDA-authorized test. Patients with any degree of hepatic impairment or cirrhosis are contraindicated, as are patients whose platelet count is under 100,000 per microliter before treatment. Physicians will quantitative-test surface antigen up front, because the 3,000 cutoff separates responders from the rest: someone at 400 IU/mL sits in the highest-response subgroup, while someone at 2,900 counts as eligible but with lower expected odds. GSK licensed bepirovirsen from Ionis, and both companies have regulatory decisions pending in additional countries, so the eligible population expands only as those reviews conclude.

The Boxed Warning Explained

The FDA approved the drug with a boxed warning, the agency’s strongest safety flag, covering two named risks. On-treatment hepatic flares are marked rises in the liver enzyme ALT, in some cases 20 to 40 times the upper limit of normal, mostly appearing within the first twelve weeks and generally resolving when the drug is interrupted or stopped. Thrombocytopenia is the second: sudden, unpredictable drops in platelets that can be life-threatening, which is why platelet counts must be checked before the first dose and monitored weekly, with permanent discontinuation below 50,000. The label also flags a gradual decline in kidney filtration (eGFR) that is usually reversible after discontinuation, and warns against use in patients coinfected with hepatitis D. Separately, the label requires frequent monitoring for at least one year if nucleos(t)ide therapy is stopped after the course, because severe hepatitis flares can occur then. In plain terms: the upside is a cure attempt, the cost is hands-on lab monitoring by a specialist.

Why a 19% Rate Restructures the Field

Nineteen percent sounds modest until it is compared with what came before. Standard suppressive therapy, nucleos(t)ide analogs taken indefinitely, reaches a functional cure at a rate the GSK release places under 1% after a year of treatment. Interferon approaches have helped some patients but carry a heavy side-effect burden. Against that baseline, one in five eligible adults stopping all medication within six months, with self-administration possible after the first dose, moves functional cure from pathology-lab goal to clinical agenda. Hepatologists quoted in coverage, including Dr. Norah Terrault of USC Keck, called it the start of a new era for a disease where a generation of drug development successfully suppressed HBV DNA but rarely cleared surface antigen, which is the true obstacle to calling anyone cured.

What Happens Next

Three threads are now live. First, access: pricing and payer coverage have not been published in the coverage reviewed here, and with a specialist-administered injectable and required monitoring, reimbursement grids will decide how quickly the eligible group in the United States, roughly 1.7 million people, gets treated. Expect insurers to build prior-authorization templates around the exact label criteria: cirrhosis-free, six months on NrtI, suppressed DNA, quantified HBsAg. Second, patient selection research will sharpen, because adverse-event management depends on catching flares and platelet drops early, and the monitoring cadence in the label effectively writes the protocol US hepatologists will follow. Third, the regulatory pipeline continues: GSK says decisions are anticipated in coming months across other geographies, and Hibsago’s first global approval came in Japan in August 2026, making the US the second market. For patients, the move this week is not to self-refer for injections; it is to ask a hepatologist for a quantitative HBsAg test, because that one number determines whether this path even opens.

Frequently Asked Questions

Who qualifies for Hibsago?

Adults without cirrhosis who have been on nucleos(t)ide therapy for at least six months, have suppressed HBV DNA, and have hepatitis B surface antigen measured at 3,000 IU/mL or below on an FDA-authorized test.

What is a functional cure for hepatitis B?

It means HBV DNA and the surface antigen (HBsAg) are undetectable for at least 24 weeks after stopping all treatment, indicating the immune system controls the virus without medication.

How well does bepirovirsen work?

In pooled phase 3 B-Well trials, 19% of treated adults achieved functional cure within six months (233 of 1,220, versus none in the placebo group), and 26% among those whose starting surface antigen was at or below 1,000 IU/mL.

Sources:

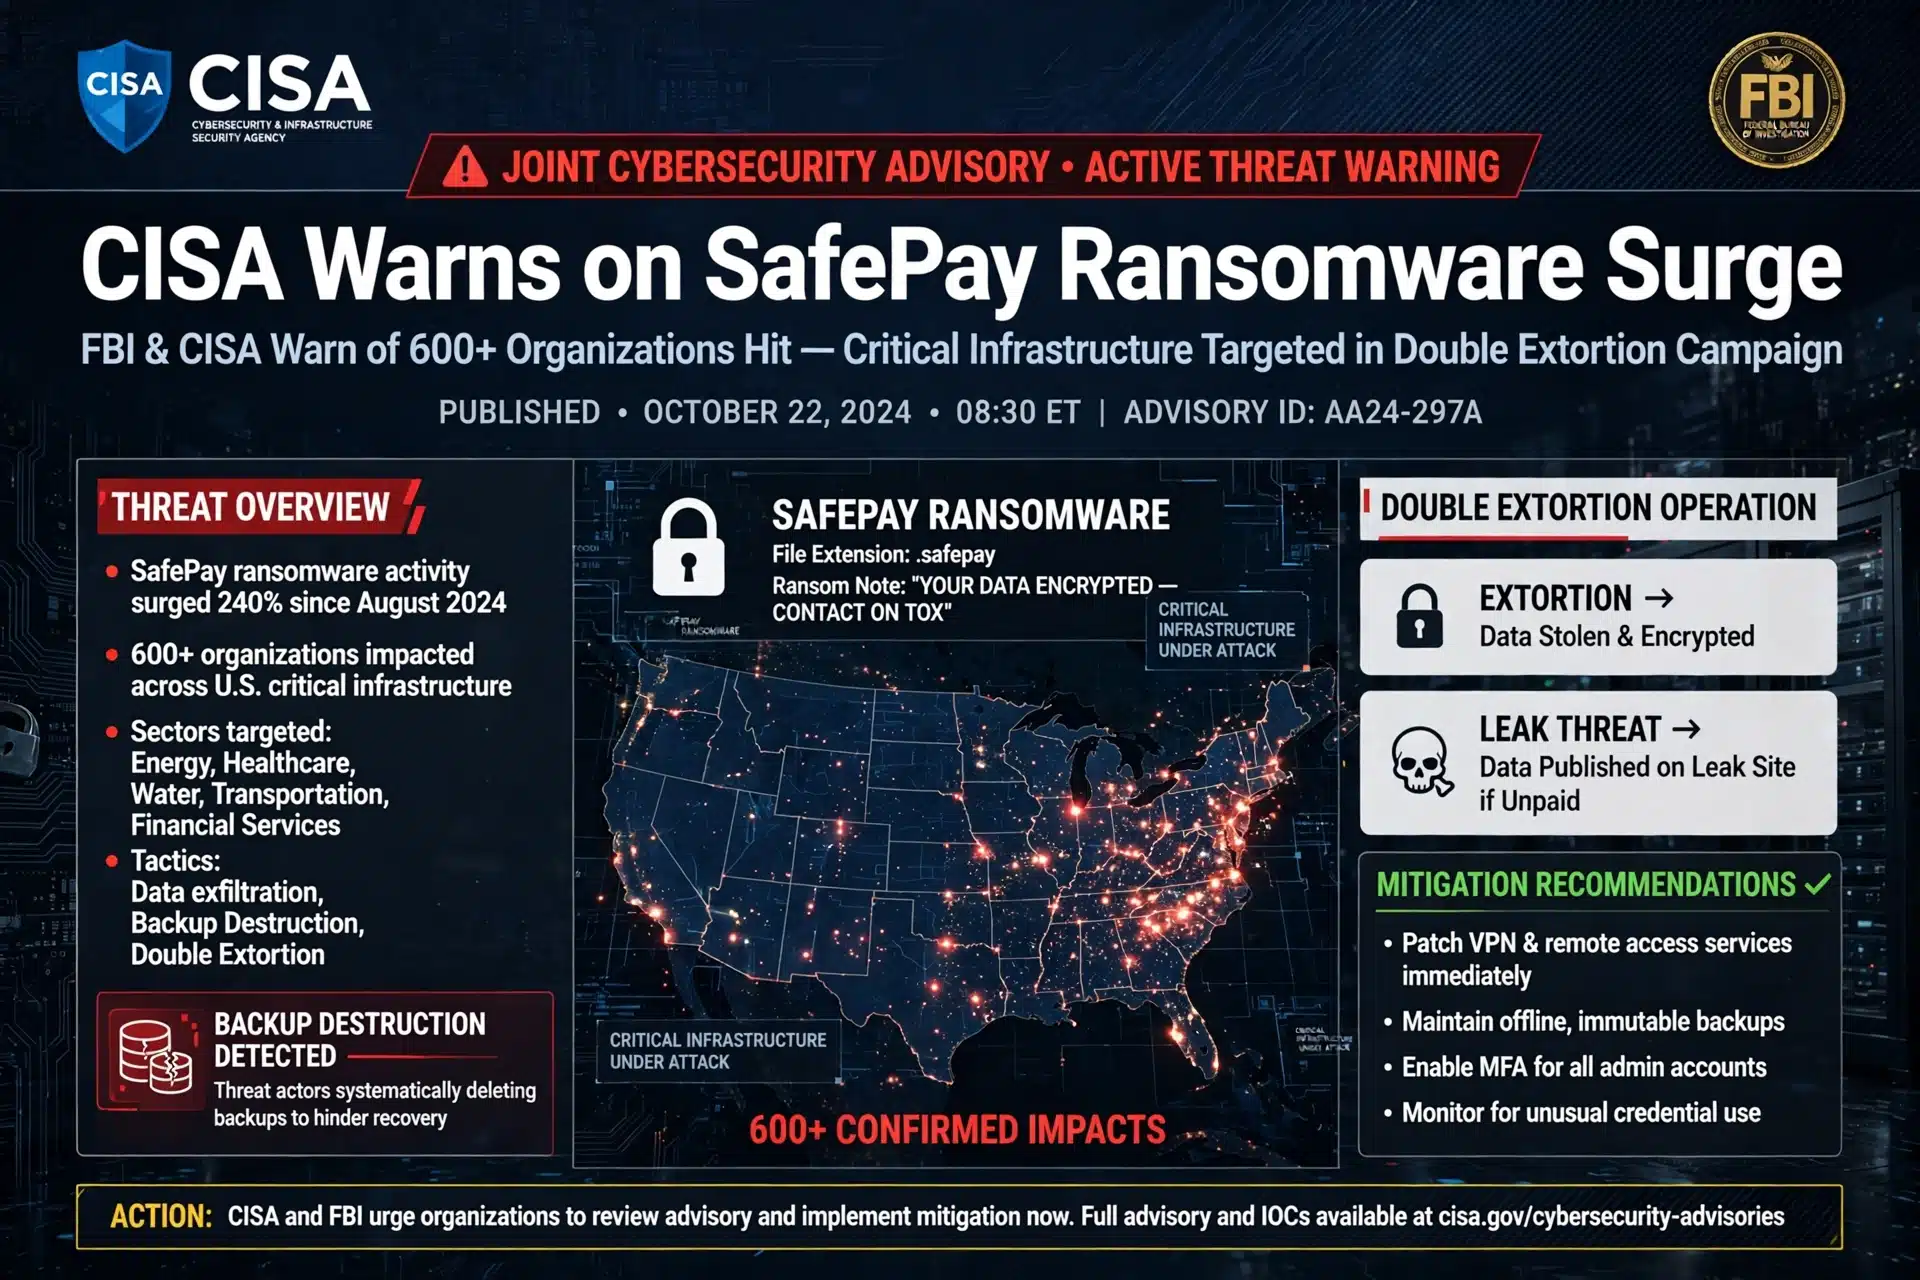
CISA and FBI Issue Joint SafePay ransomware Advisory: 600 Victims, 5 Known Flaws

Six agencies published a joint SafePay ransomware advisory on October 20, 2026, warning that the group has hit at least 600 separate victims across US and allied critical infrastructure since August 2024, and naming the five known exploited vulnerabilities defenders should patch first. The advisory, labeled AA26-293A, comes from the FBI, CISA, the US Secret Service, Germany’s LKA Rheinland-Pfalz and two UK units, and it lands as SafePay has become one of the most active ransomware brands of 2026. Here is what the advisory says the group does, the exact flaws in play, and what a US organization should do this week.

Key Takeaways:

  • – Joint advisory AA26-293A on SafePay ransomware was released October 20, 2026 by CISA, FBI, USSS and international partners.
  • – SafePay has impacted at least 600 separate victims since August 2024, including businesses and critical infrastructure.
  • – Five exploited flaws are named, all in edge and backup products: two Cisco ASA/FTD CVEs, two Veeam CVEs and one SonicWall SonicOS CVE.
  • – Initial access usually comes from stolen or guessed passwords, plus brute force and phished account profiles.
  • – Data is exfiltrated before encryption with RClone, WinSCP, FileZilla or Backblaze tools, then files are renamed with the .SafePay extension.

Who SafePay Is and How It Gets In

The advisory describes a mature operation rather than an opportunistic crew. SafePay actors have been highly active since August 2024, and the authors say the group typically gains access by stealing or guessing passwords. Techniques listed include brute forcing (T1110) and use of phished account profiles, along with VPN access sourced from IP addresses belonging to the Mullvad provider, a detail that means seeing Mullvad egress on a VPN log is not automatically benign in your environment. None of this is exotic: it is the standard playbook of credential-first intrusion, executed against an unusually wide victim base that scales across businesses and critical infrastructure sectors.

What distinguishes SafePay procedurally is the discipline of its double extortion. Actors copy data out before encrypting anything, using RClone, WinSCP, FileZilla and Backblaze’s b2.exe, then lock files and rename them with the .SafePay extension. Non-payers’ data is posted to the group’s leak site, and victims are driven to a chat portal on a TOR address to negotiate. Brandefense’s analysis of the advisory also notes that actors sometimes deleted all network-attached backups, which elevates backup hygiene from a checklist item to the difference between a ransom decision and a restore decision.

The Five Flaws and What to Patch

All five exploited vulnerabilities are already in the CISA Known Exploited Vulnerabilities catalog, flagged for known ransomware use. The advisory names the CVEs; vendor advisories supply the products and fixes.

  • – CVE-2020-3259, Cisco ASA and FTD: an unauthenticated attacker can read device memory with a crafted request on certain AnyConnect and WebVPN configurations. Fixed in ASA 9.8.4.20 and later listed branches; Cisco lists no workaround, so upgrade is the only door-close.
  • – CVE-2023-20269, Cisco ASA and FTD remote access VPN: brute-force of valid usernames and passwords, not an authentication bypass. MFA on every VPN account and limiting failed logins materially blunts it.
  • – CVE-2023-27532, Veeam Backup and Replication: an unauthenticated network user can pull encrypted credentials from the configuration database. Fixed in 12.0.0.1420 (P20230223) and 11.0.1.1261 (P20230227); blocking inbound TCP 9401 buys time until patching.
  • – CVE-2024-40711, Veeam Backup and Replication: unauthenticated remote code execution with a 9.8 CVSS on 12.1.2.172 and earlier 12.x builds. Fixed in build 12.2.0.334, and the backup server should not face the internet regardless.
  • – CVE-2024-40766, SonicWall SonicOS: improper access control in management access, affecting Gen 5, 6 and early Gen 7 firmware. Patch per advisory SNWLID-2024-0015 and keep firewall management off the open internet.

The advisory adds that actors exploited the Veeam and SonicWall flaws on internet-exposed systems using automated scripts, and used the Cisco edge flaws after landing through phished account profiles. Translation for patch teams: the internet-facing perimeter and the backup server are the two crown boxes, in that order.

Why the Timing Matters for US Organizations

SafePay is not a new name in incident response circles, but a six-agency advisory is a different signal than a vendor profile. Joint US-Ukin… US-UK-German advisories generally follow a period in which the group’s tradecraft stabilized and its victim count made it a named priority, which is where SafePay has been through 2026: among the most active ransomware operations of the year. Companies running Cisco edge gear, Veeam backups or SonicWall firewalls should treat the advisory as a work order dated October 20, not as background reading, because the catalog status of the five CVEs gives federal contractors a hard patching deadline on November 3, 2026, two weeks from the advisory date.

The Controls That Beat the Group

Patching closes five doors, but the advisory’s core defense list is older than SafePay and more durable than any single CVE. Require MFA, especially for webmail, VPNs and accounts on critical systems. Use long passwords, 15 to 64 characters, with no reuse and lockouts after failed attempts. Keep encrypted, immutable, offline backups and test the restore, because the group deletes backups before encrypting. Segment networks and run EDR to catch lateral movement. Audit domain controllers, servers and Active Directory for accounts nobody recognizes, and alert when security tooling is stopped or modified, since the advisory even lists tool-disabling (T1685) as a named behavior to watch for.

For a small IT team, the week’s realistic priority list: inventory which of the five products you run and at what versions, apply the fixes above, force MFA on every VPN account, and verify one backup copy is unreachable from the domain. If any of the named flaws was open on an internet-facing system before the patch, treat that system as a possible intrusion and review its accounts, logs and scheduled tasks before assuming you were not touched.

What Happens Next

Expect the SafePay saga to ripple three ways. Federal contractors face the November 3 patching deadline for the cataloged CVEs, and the advisory gives auditors a ready-made checklist. Fortune 500 boards will ask their CISOs the uncomfortable version of this week’s question, which is not what does SafePay exploit but whether our backup server is internet-reachable, a question the answer should have been no for years. And expect copycat crews to fold the same five CVEs into their own exploit chains, a pattern seen after every major joint advisory, which is why the patching urgency extends to any organization still unpatched on Cisco ASA, Veeam or SonicWall products even if it has never heard of SafePay. The group’s 600-victim run through this quarter shows the door was often left open; this advisory finally prints the address of the door.

Frequently Asked Questions

What is SafePay ransomware?

SafePay is a ransomware group active since August 2024 that steals or guesses passwords, copies data with cloud tools, encrypts files with the .SafePay extension and posts non-payers’ data to a leak site. It has hit at least 600 victims.

Which vulnerabilities does SafePay exploit?

The advisory names two Cisco ASA/FTD flaws (CVE-2020-3259, CVE-2023-20269), two Veeam Backup and Replication flaws (CVE-2023-27532, CVE-2024-40711) and one SonicWall SonicOS flaw (CVE-2024-40766), all in CISA’s known-exploited catalog.

What should my organization do first?

Patch the five flaws, enforce MFA on VPNs and webmail, verify an immutable offline backup exists, and audit Active Directory for unrecognized accounts; treat any previously internet-exposed vulnerable system as possibly compromised.

Sources: